Governance Console & Unified Audit
Every subdocument characterization match, freshness cluster assignment, metapolicy decision, and cross chain principal trace converges into CaberUserConsole. The console provides security engineers, governance operators, and platform administrators with a unified web control plane for visual policy authoring, live telemetry inspection, API and tool discovery, provenance graph exploration, and system health diagnostics.
Dedicated Caber User Console Guide
For comprehensive page by page operator guides, interactive subview walkthroughs, and light and dark mode screenshots of every screen in the console, see the dedicated Caber User Console top level section:
- Console Overview & Navigation: Deployment selector (
/), preview agreement modal, topbar, sidebar navigation, and the contextual Ask AI Assistant drawer. - Dashboards & Observability: Home overview (
/admin/home), Object Clusters & Versions (/admin/overlapping), Ingest Performance (/admin/scanning), Platform Status (/admin/platform), and Context Graph Explorer (/admin/contextGraph). - Session Audit & Forensics: Multi turn conversation grouping (
/admin/audit), Trace Detail Balloon view, inline Governance Decision evidence, surgical redaction highlights, Execution Waterfall, and Causal Provenance Graph. - API & Tool Interception: End to end workflow from passive and wire discovery (
/admin/discovery) and inline payload layout confirmation (LayoutConfirmPanel) toApiMaproute rules (/admin/config/api-mappings). - Policy & Source Configuration: Policy Studio and
Wasmbundle activation (/admin/config/policies), SDK fleet bindings (/admin/config/sdk-deployments), Identity Sources (/admin/config/identity-sources), Object Sources (/admin/config/object-sources), and AI config validation (/admin/config/review). - Console Engineering & Extension: Internal engineering architecture, Next.js
BFFroutes, semantic color tokens, and three gate style and contrast lint checks.
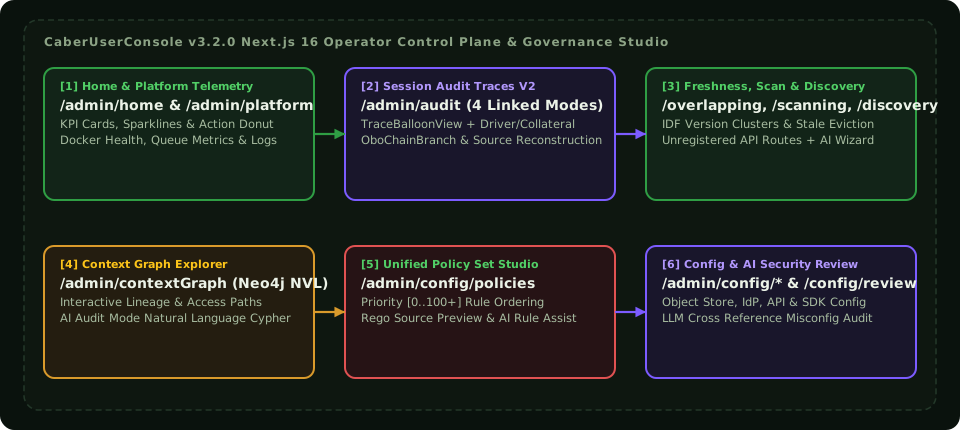
While caber_core and pycaber(auto) operate in band inside application processes and gateways, human operators use the out of band console command center to:
- Inspect Unified Audit Trails (
/admin/audit): Correlate LLM prompts, tool executions, WRL Chunker fragment hits, On Behalf Of (OBO) principal delegation chains, and metapolicy verdicts in one timeline. - Discover and Intercept APIs & Tools (
/admin/discoveryand/admin/config/api-mappings): Identify shadow HTTP APIs,MCPtool servers, vector databases, and object stores from live wire traffic, confirm JSONPath semantic roles (ITEMS,TEXT,ID,SCORE,INPUT,OUTPUT,ERROR), and promote endpoints into governedApiMaprules. - Explore Data Lineage & Freshness Clusters (
/admin/overlappingand/admin/contextGraph): Visualize IDF document version DAGs (Original Candidate,Caber Used,Latest Version), policy boundary hulls, side by siden-merdiffs, and Neo4j provenance graphs. - Author Policies and Manage Connectors (
/admin/config/*): Build, compile, and activateWasmgovernance bundles in Policy Studio and manage SDK deployments,Identity_Sources, andObject_Sources.
Functional Capabilities by Console Workspace
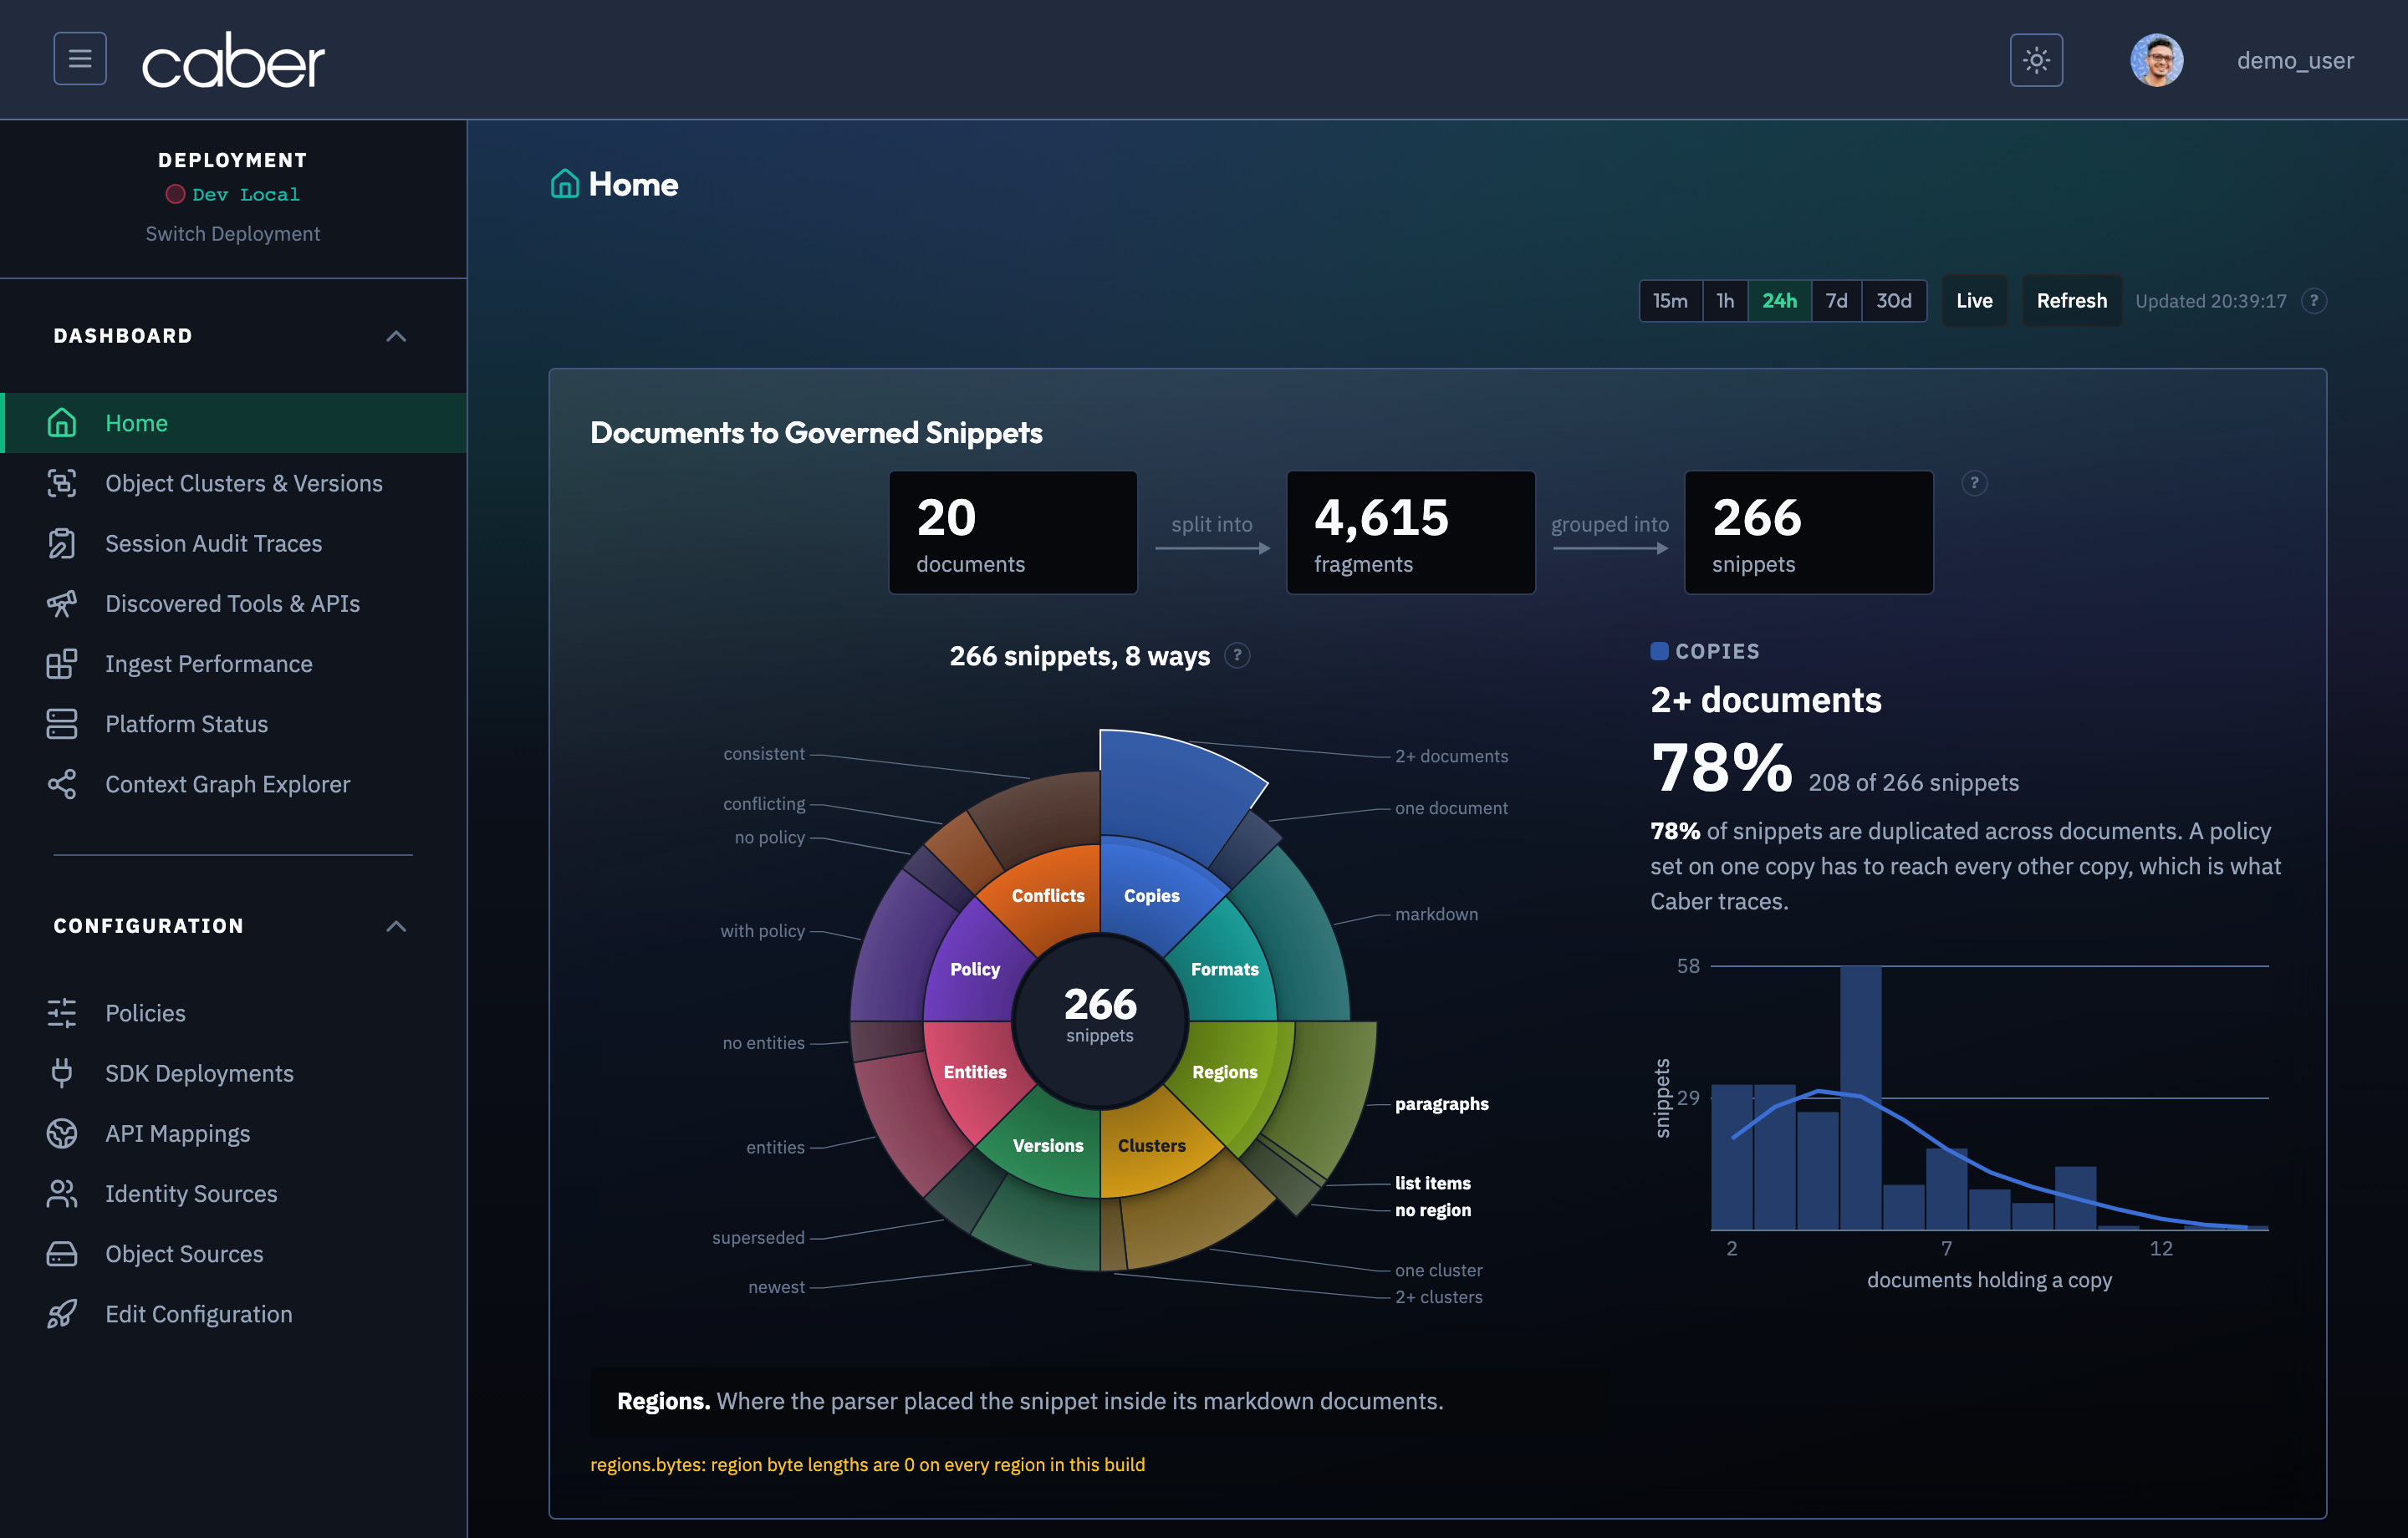
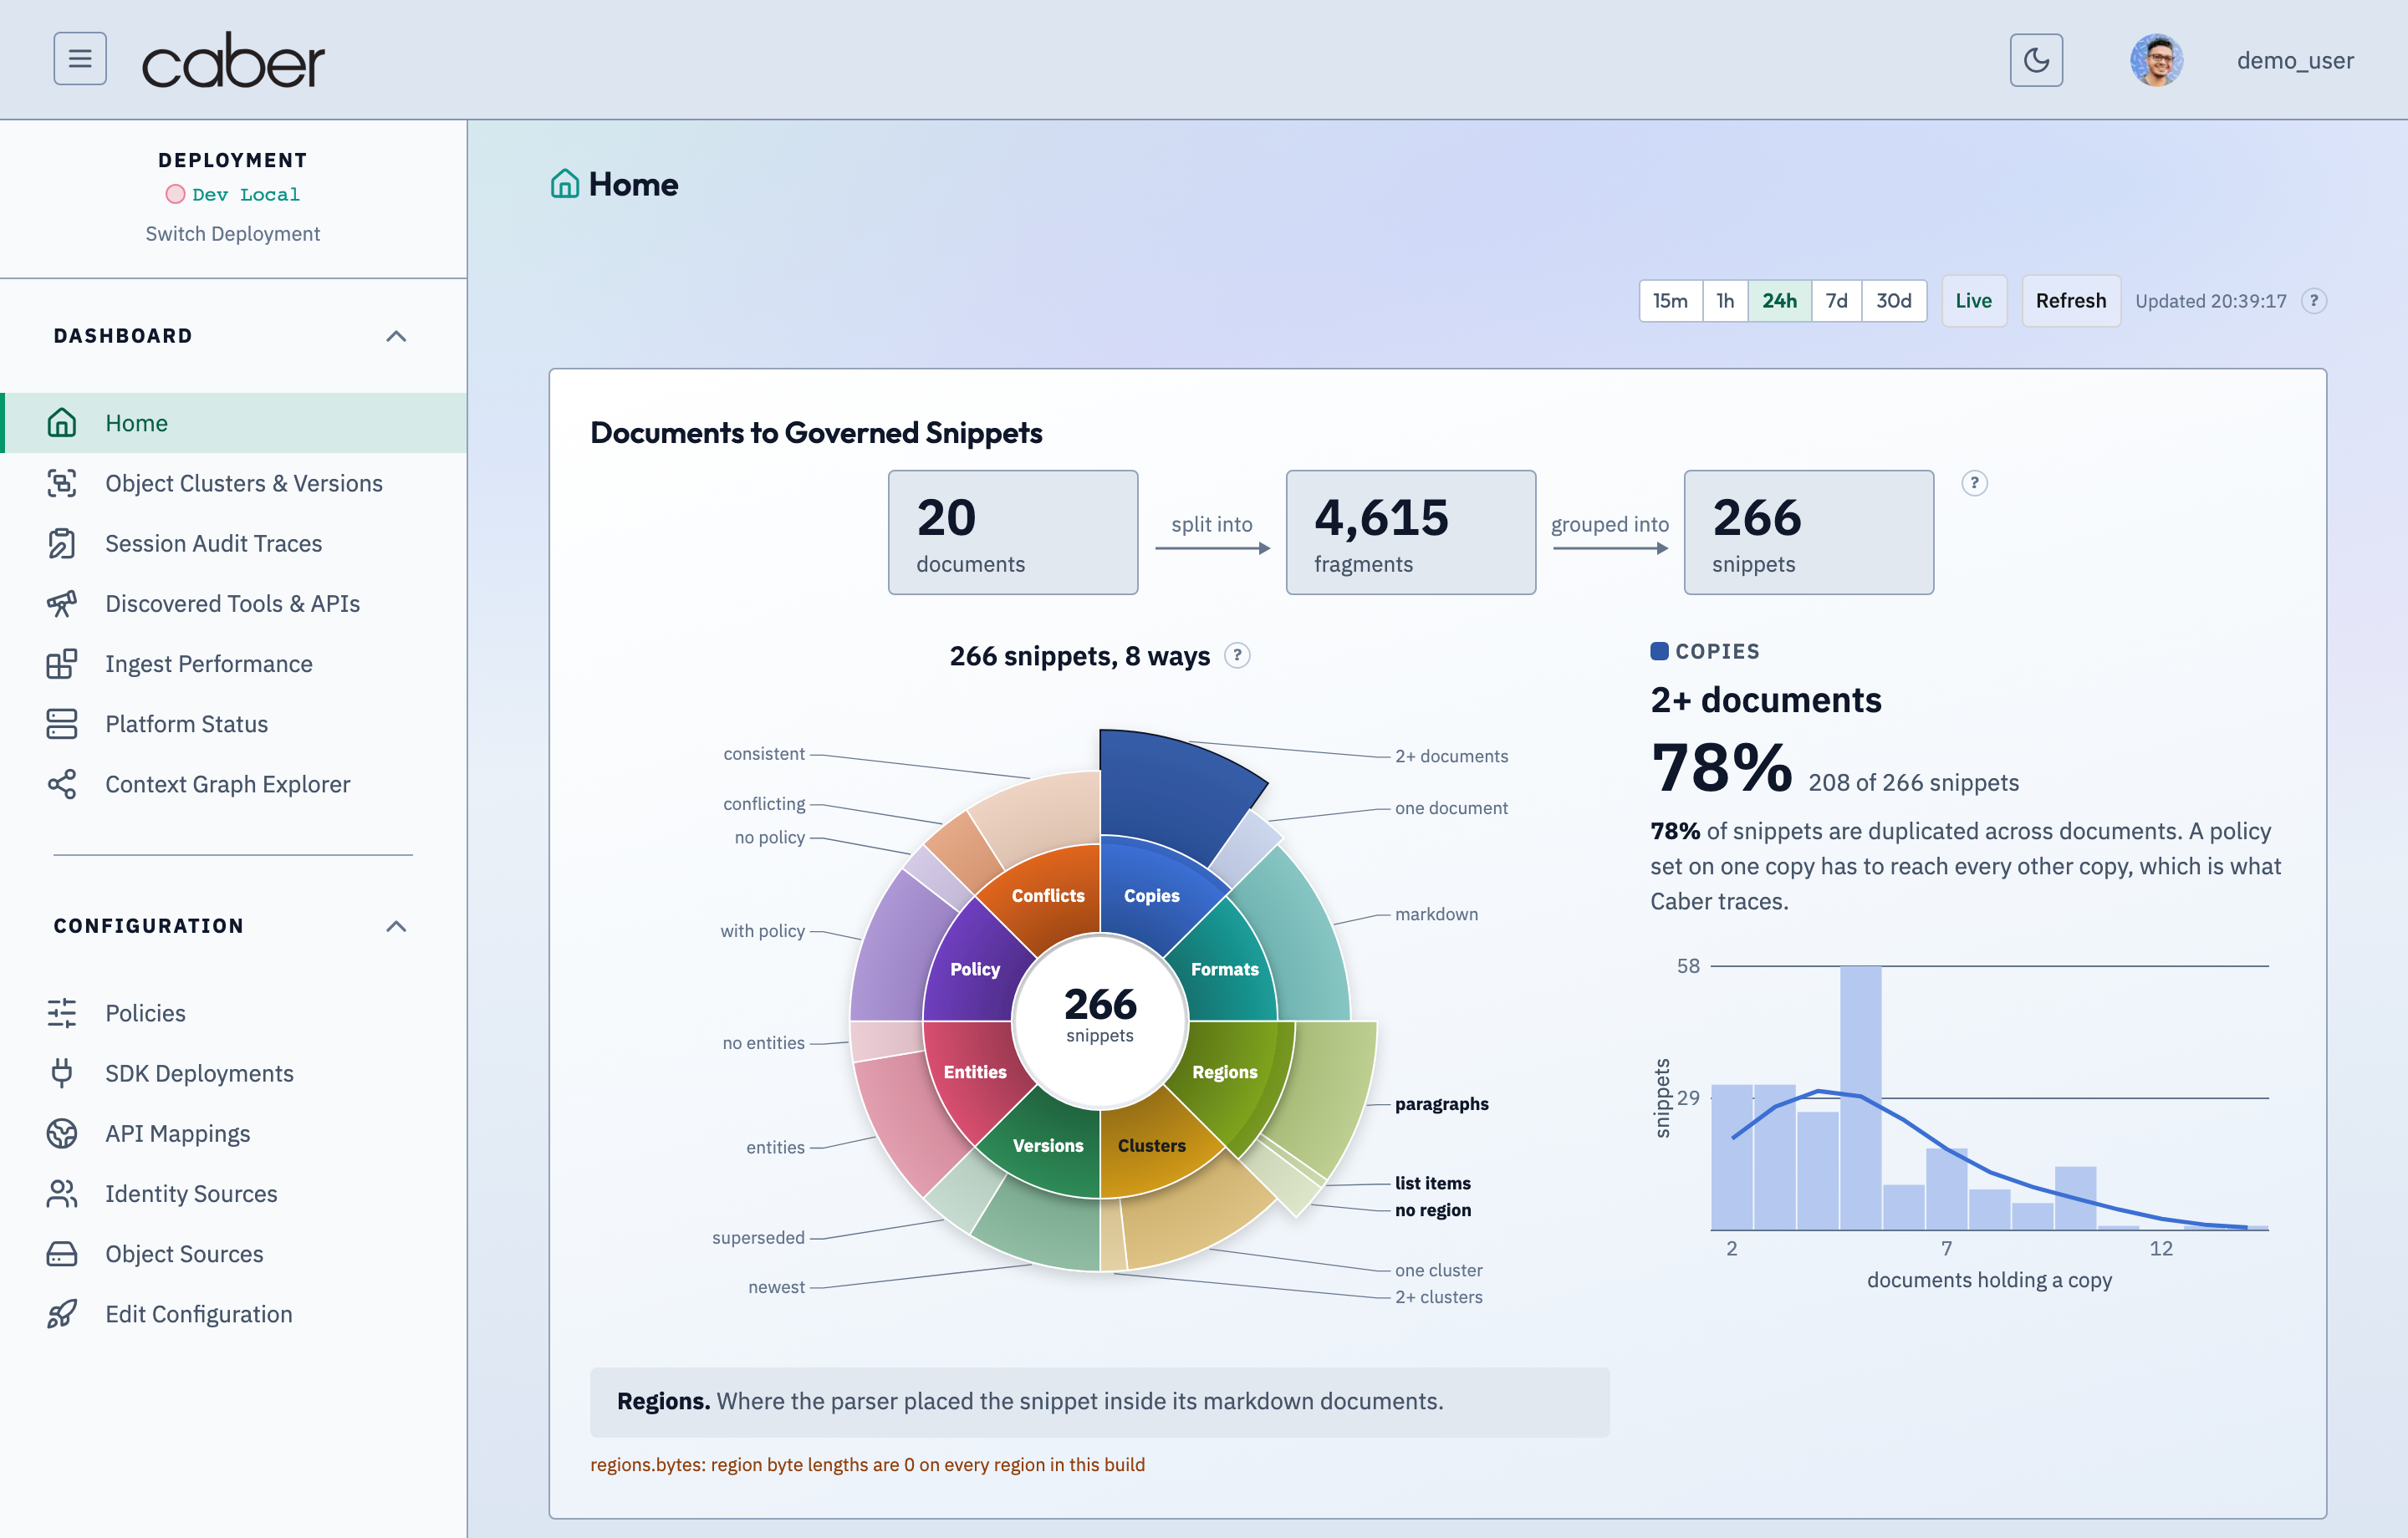
1. Executive Home, Scanning & Platform Telemetry (/admin/home, /admin/scanning, /admin/platform)
- Displays live governance KPI cards (
Interactions,Blocked / Redacted,Context Freshness,Median Latency,OBO Delegations,Active Policies), verdict timelines, latency percentile distributions (p50,p95,p99), and recent surgical redactions. - Provides dedicated observability workspaces for Ingest Performance (
/admin/scanning) and Platform Status & Logs (/admin/platform). See Dashboards & Observability for full details.
/admin/homeExecutive Overview & Four Core Governance Questions DashboardAssertion Verified: Proves that the Executive Overview dashboard synthesizes all four governance questions—data duplication, runtime policy verdicts, AI provenance traces, and platform health—into a single real-time operational command center.
2. Session Audit & Forensic Trace Inspector (/admin/audit)
- Conversation Grouping & Filters: Groups multi turn agent interactions into collapsible conversation rows, with time range presets, free text search, and secondary filters for user, API host, redaction, data edges, inference, model, operation, and tool calls. Row flags mark redacted content, linked data edges, and
OBOdelegation chains. - Trace Detail View (
Trace,Waterfall, andGraphTabs): Shows freshness, provenance, and policy together on each retrieval step (which results were current, where each came from, and which policy decided what the agent received), alongside every prompt,MCPretrieval call, surgicaldriverandcollateralredaction span, W3C execution waterfall bar, and Cytoscape causal provenance node. See Session Audit & Forensics for the complete guide.
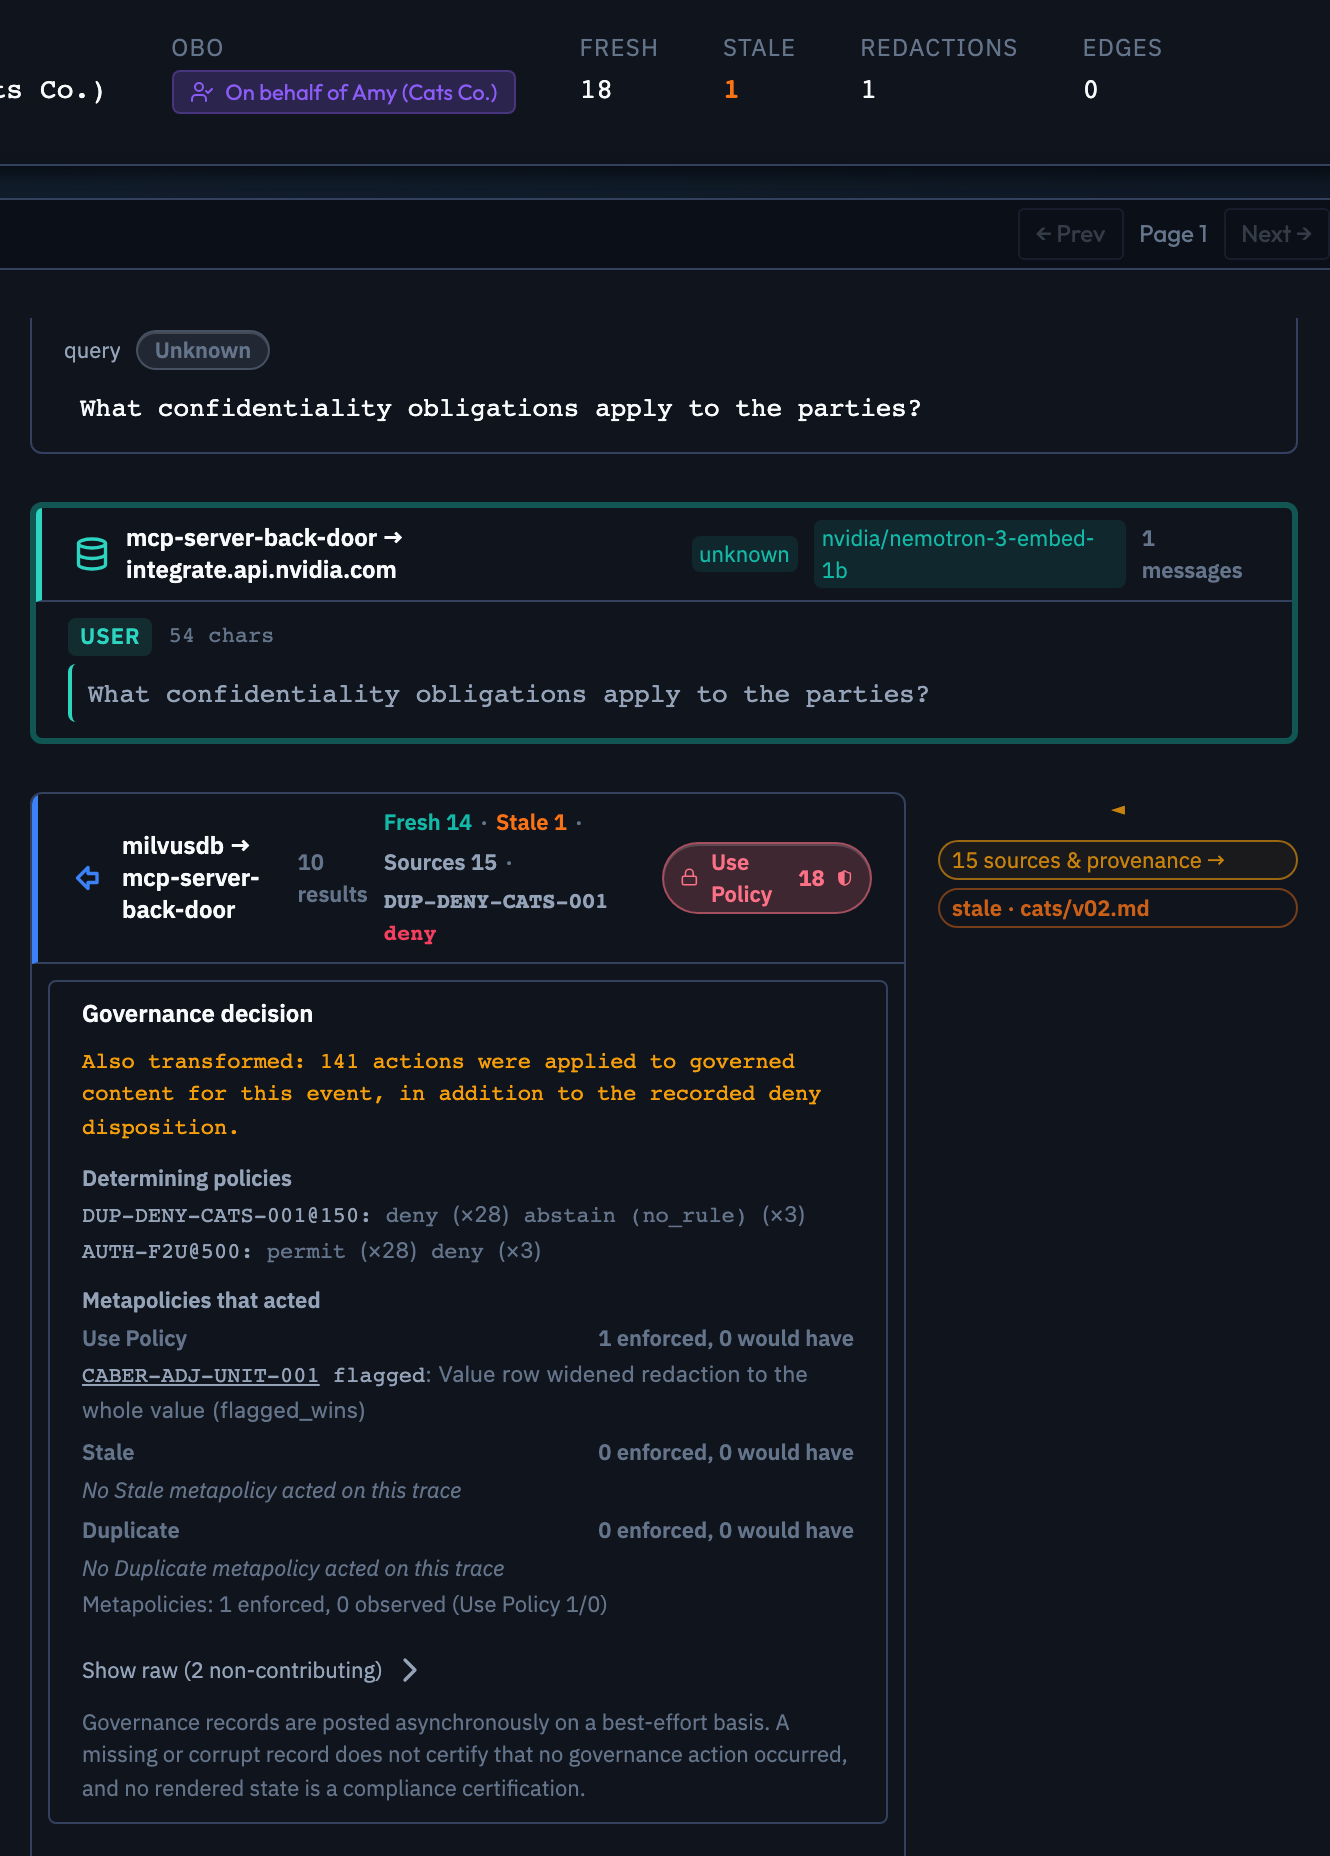
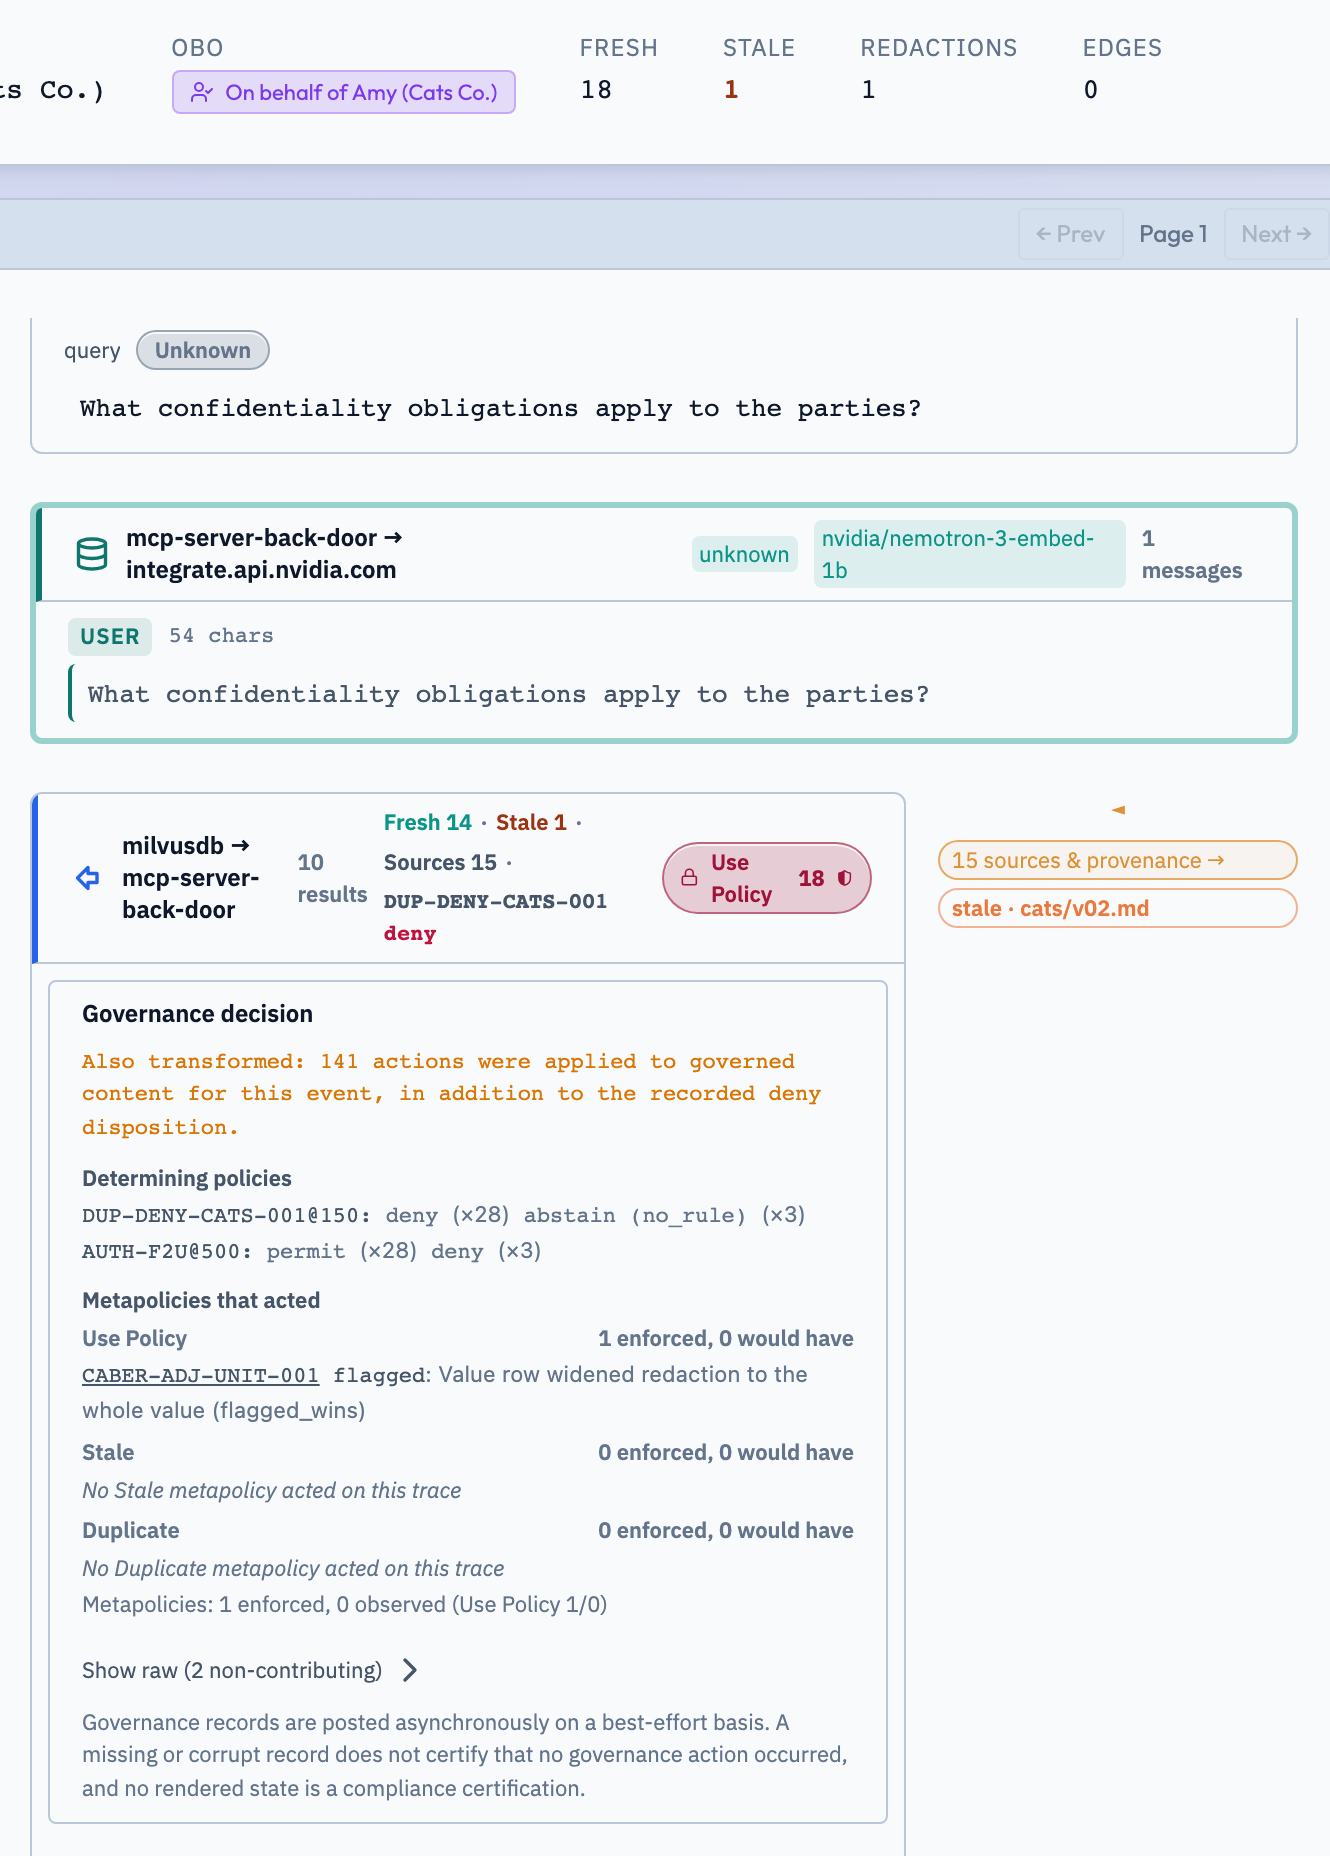
/admin/auditAudit Trace Detail: Freshness, Provenance and Policy on One Retrieval StepAssertion Verified: Proves that the console shows freshness, provenance and policy together on a single retrieval step: the evidence strip counts fresh, stale and source results, a stale chip names the source file that is out of date, a provenance chip links every source of the step to the Duplicate Tracker, and the governance panel names the determining policy, its deny verdict and which metapolicies acted.
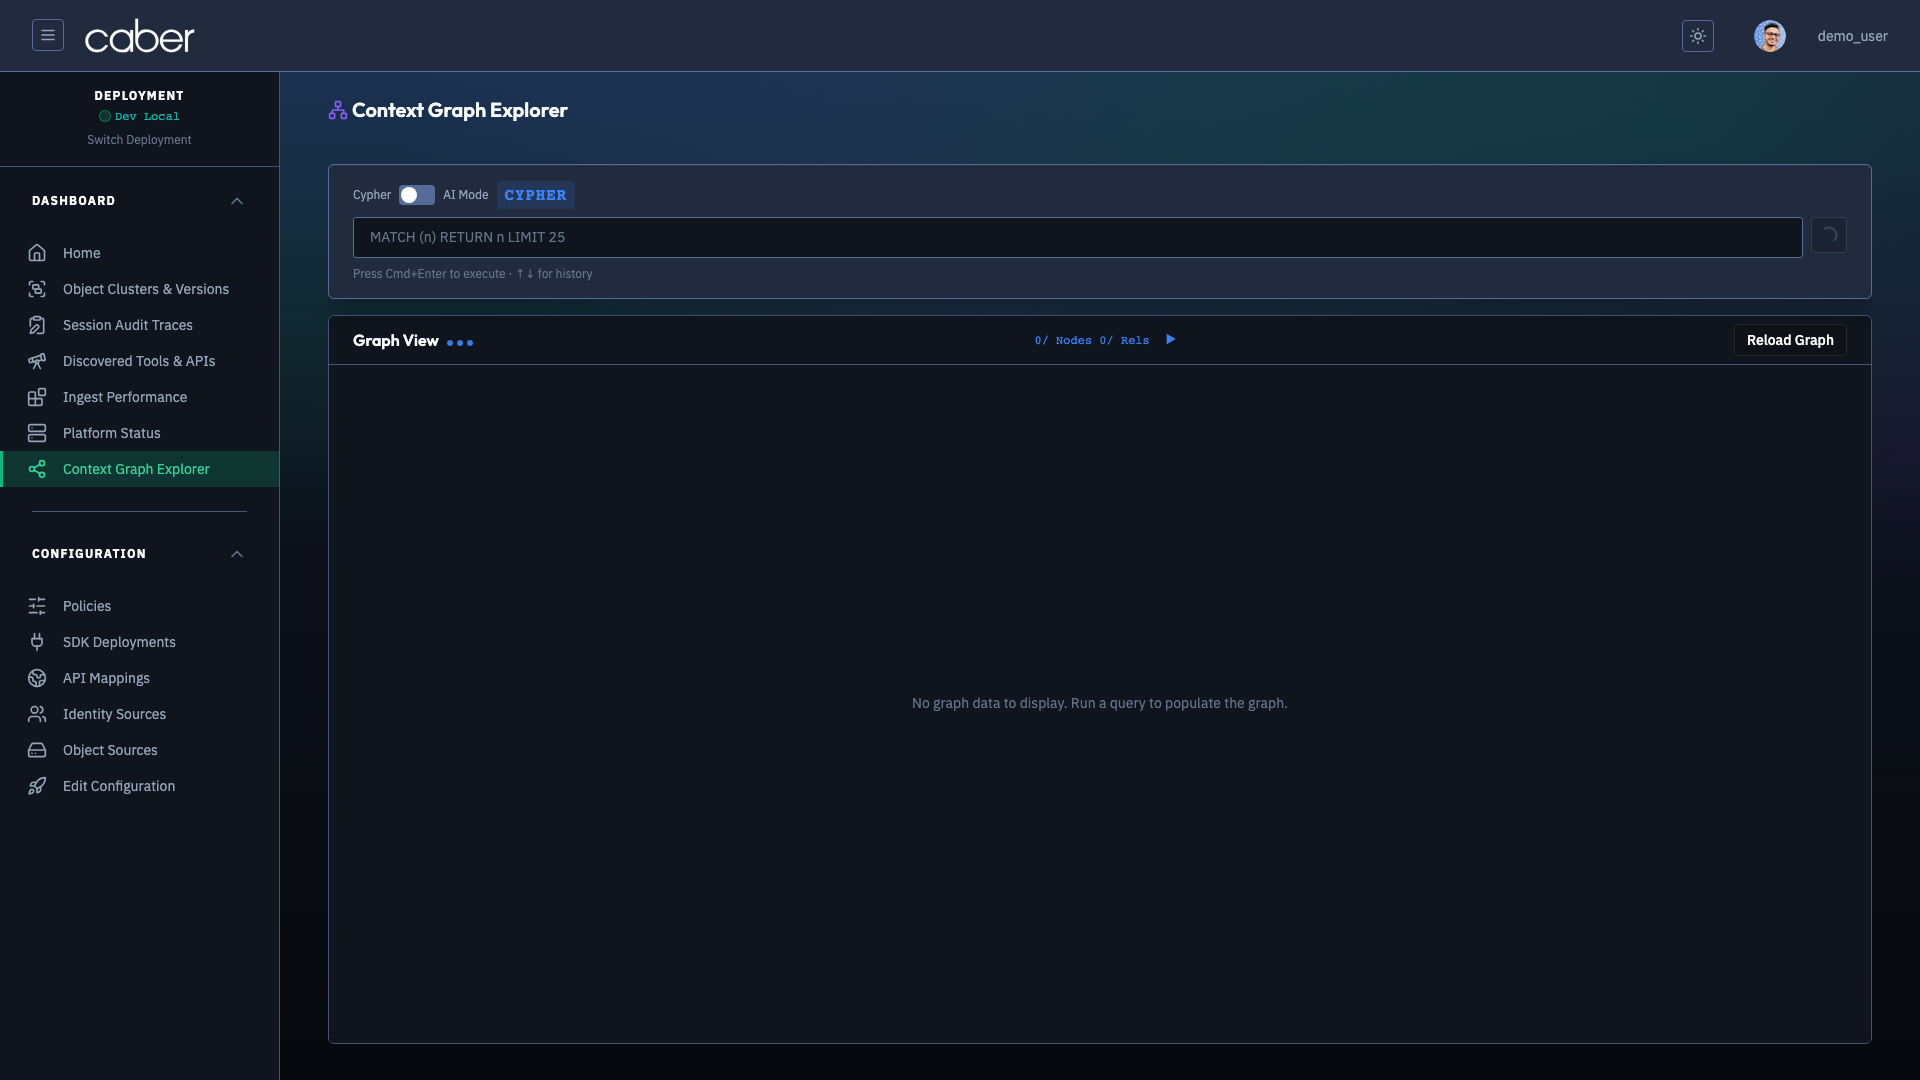
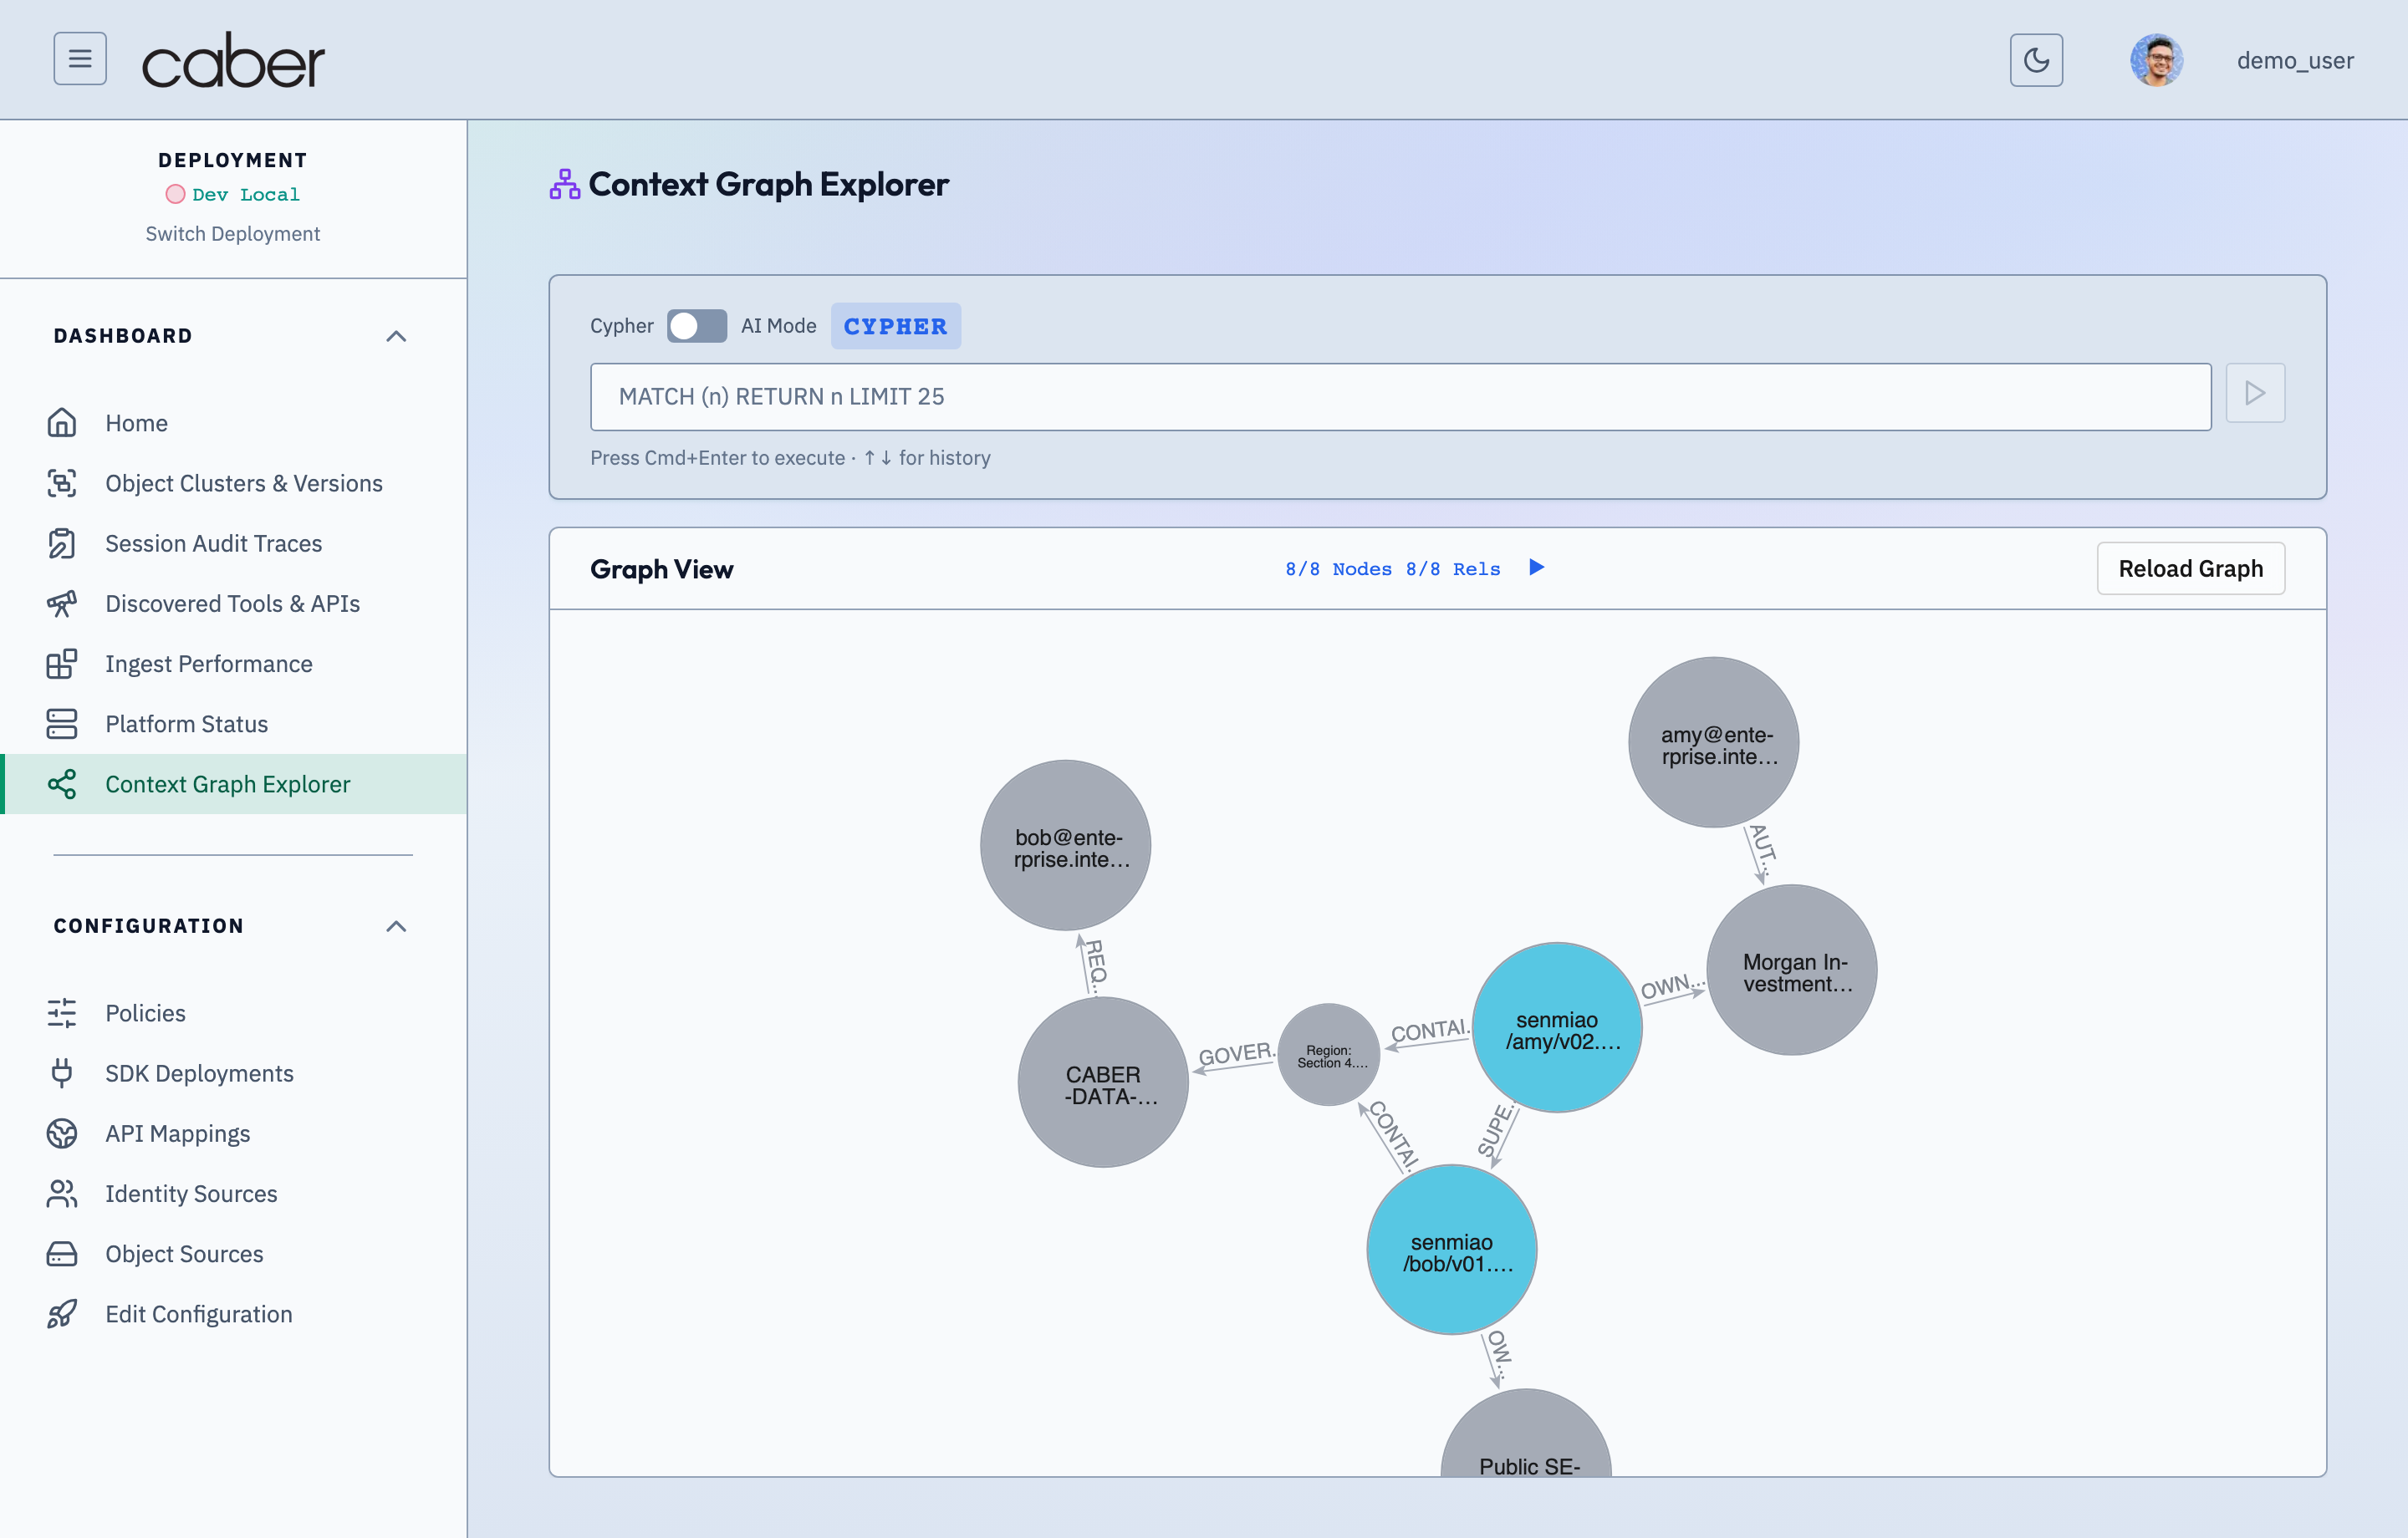
3. Object Clusters, Version DAGs & Context Graph Explorer (/admin/overlapping and /admin/contextGraph)
- Object Clusters & Versions (
/admin/overlapping): Renders the Inverse Document Frequency (IDF) version lineage DAG for every multi version document family, highlightingCaber UsedvsLatest Versionnodes, multi policy convex hulls, and side by side sharedn-merdocument comparisons (OverlapComparisonPanel). - Context Graph Explorer (
/admin/contextGraph): Interactive Neo4j graph workbench with Cypher query presets, label and relationship filters, and a sliding node inspector. See Dashboards & Observability for full details.
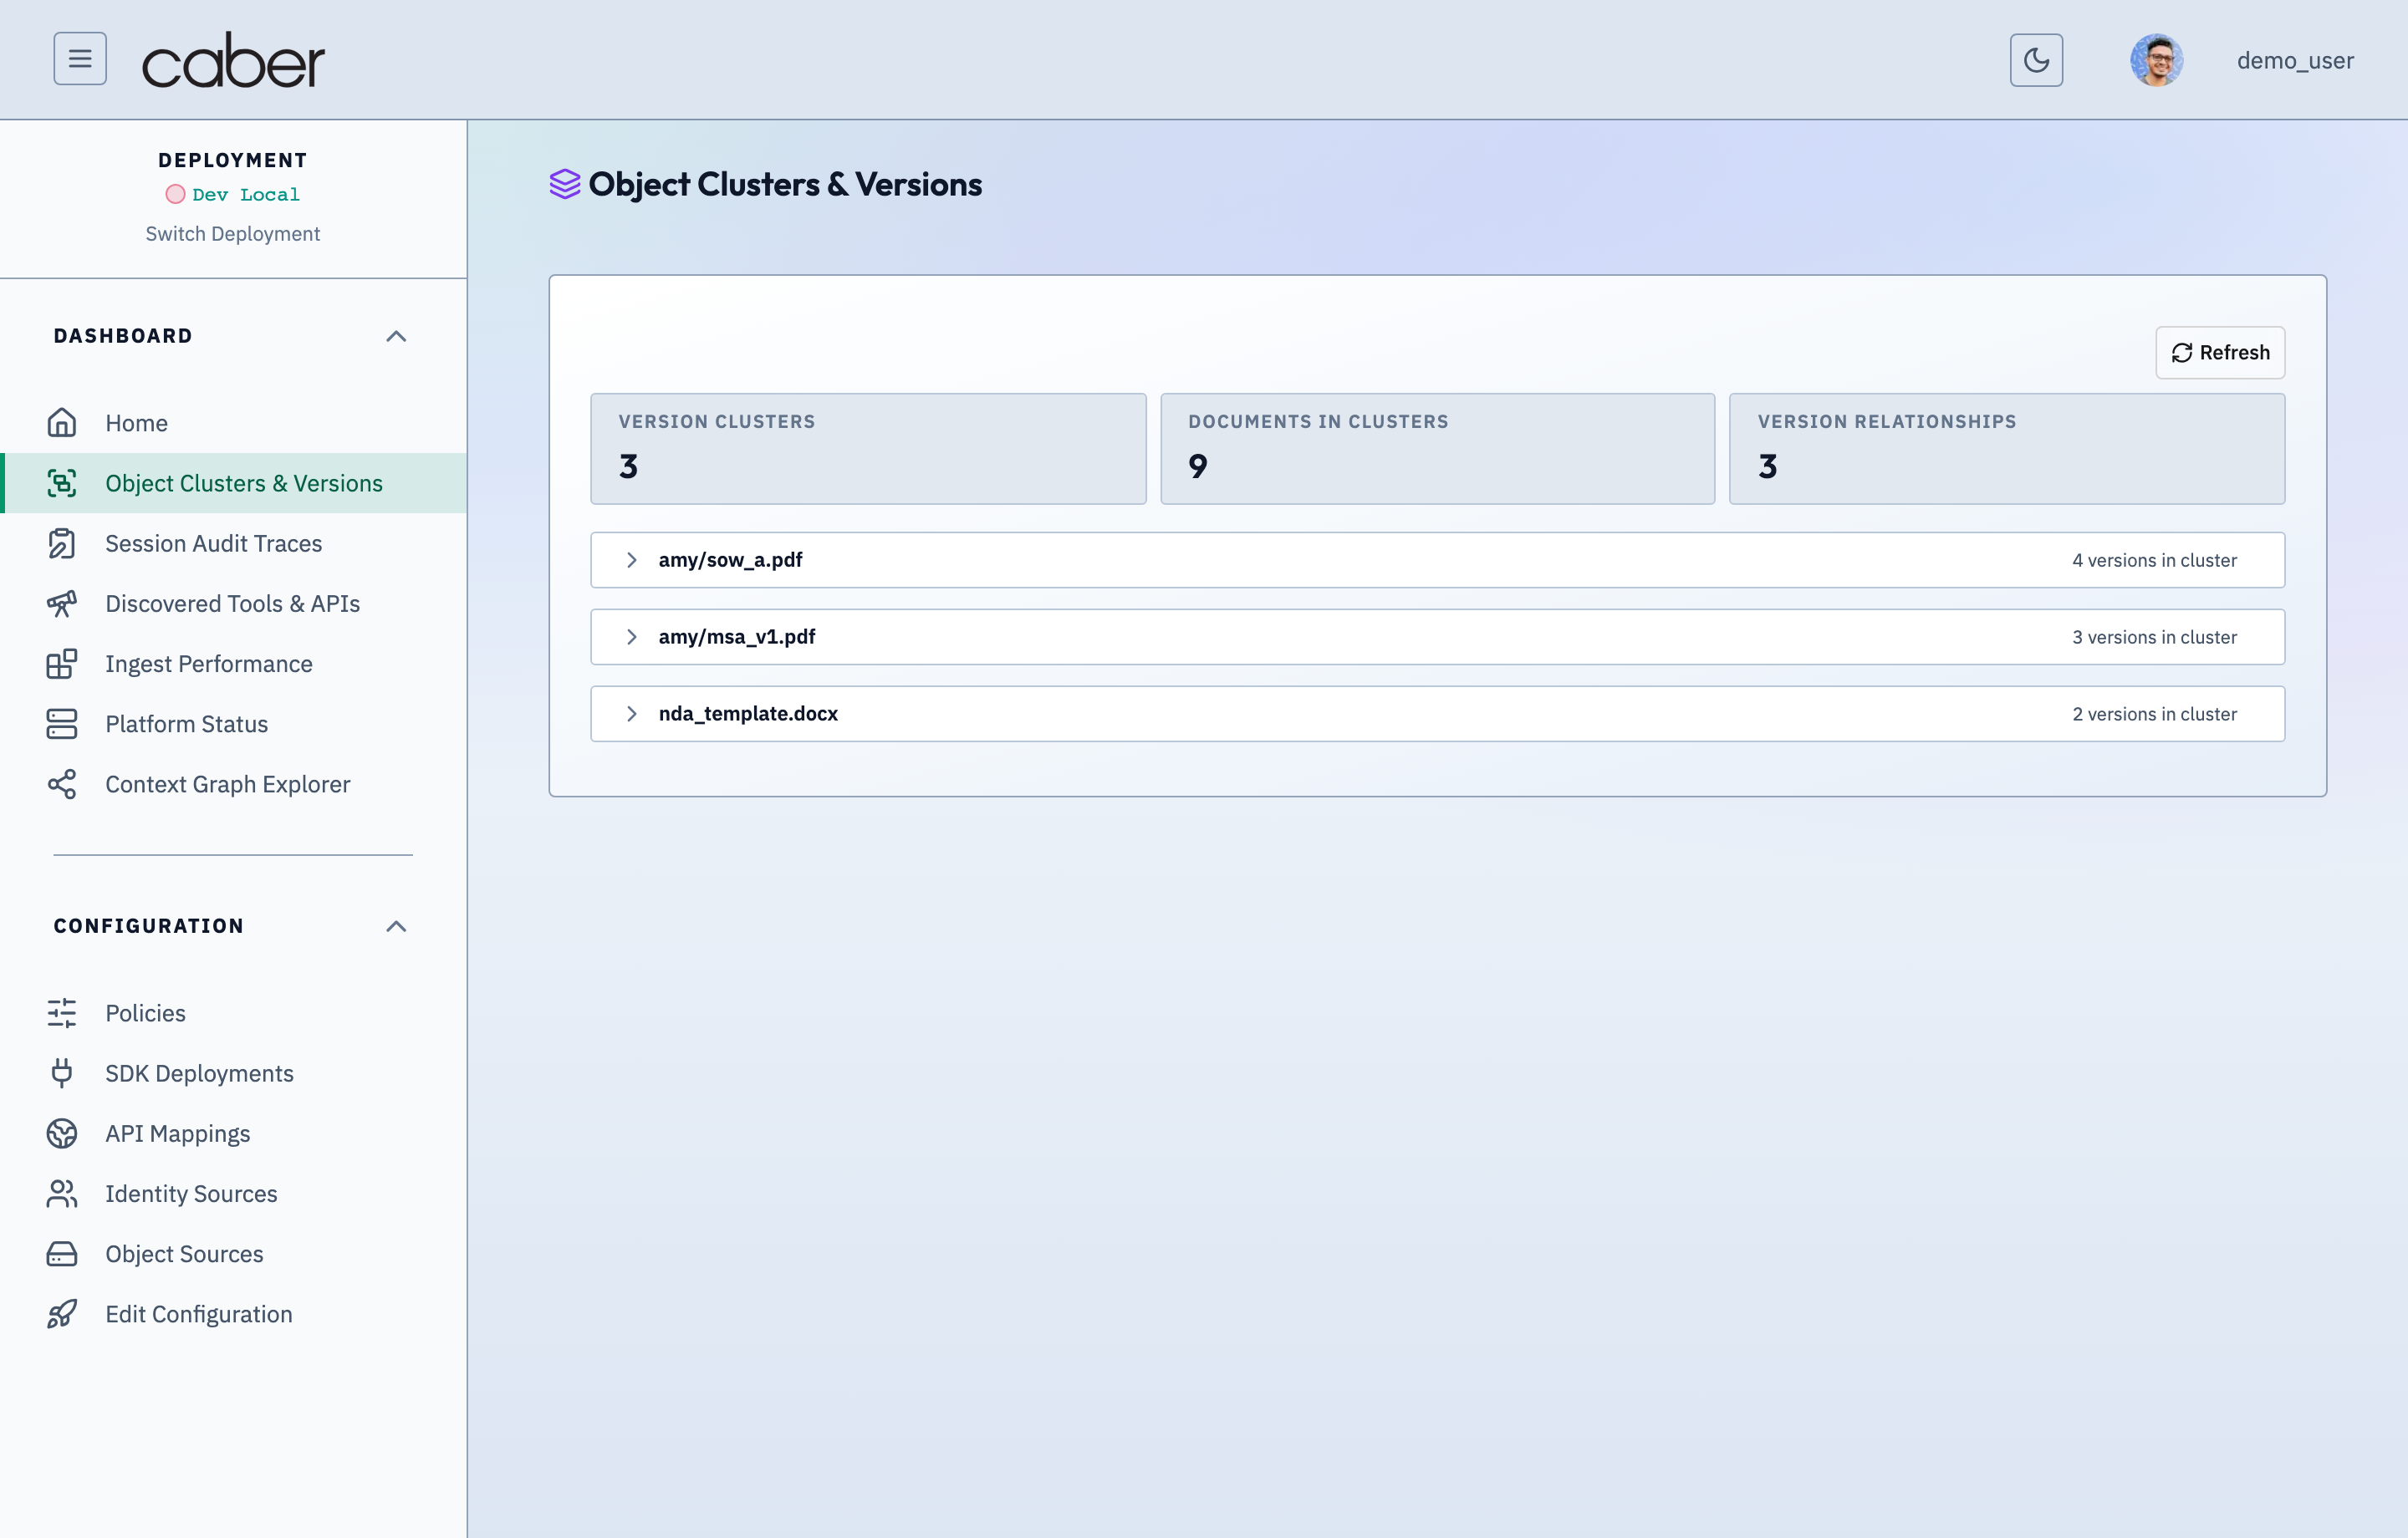
/admin/overlappingDuplicate Data Tracker & Side-by-Side Freshness Cluster InspectorAssertion Verified: Proves that Caber detects 85% to 99% enterprise content duplication down to 40-byte WRL sub-sentence phrases (97% to 98.7% coverage), separates canonical fresh sources (version_sequence == 0) from stale replicas, and enforces origin trade-secret policies even when text is copied into unlabeled channels.
/admin/contextGraphNeo4j Context Graph & Ontological Provenance ExplorerAssertion Verified: Proves that identical sentence bytes in two different documents carry distinct meaning and governance verdicts depending on their ontological neighborhood (:Region NER rollup, LNKD-{xor}-{count} equivalence class, and CORI provenance).
4. API Discovery & Interception Studio (/admin/discovery and /admin/config/api-mappings)
- Passive & Wire Resource Discovery (
/admin/discovery): Automatically catalogs outbound HTTP APIs,MCPservers, object stores, databases, and scripts observed across the deployment. - Confirm Intercept Layout (
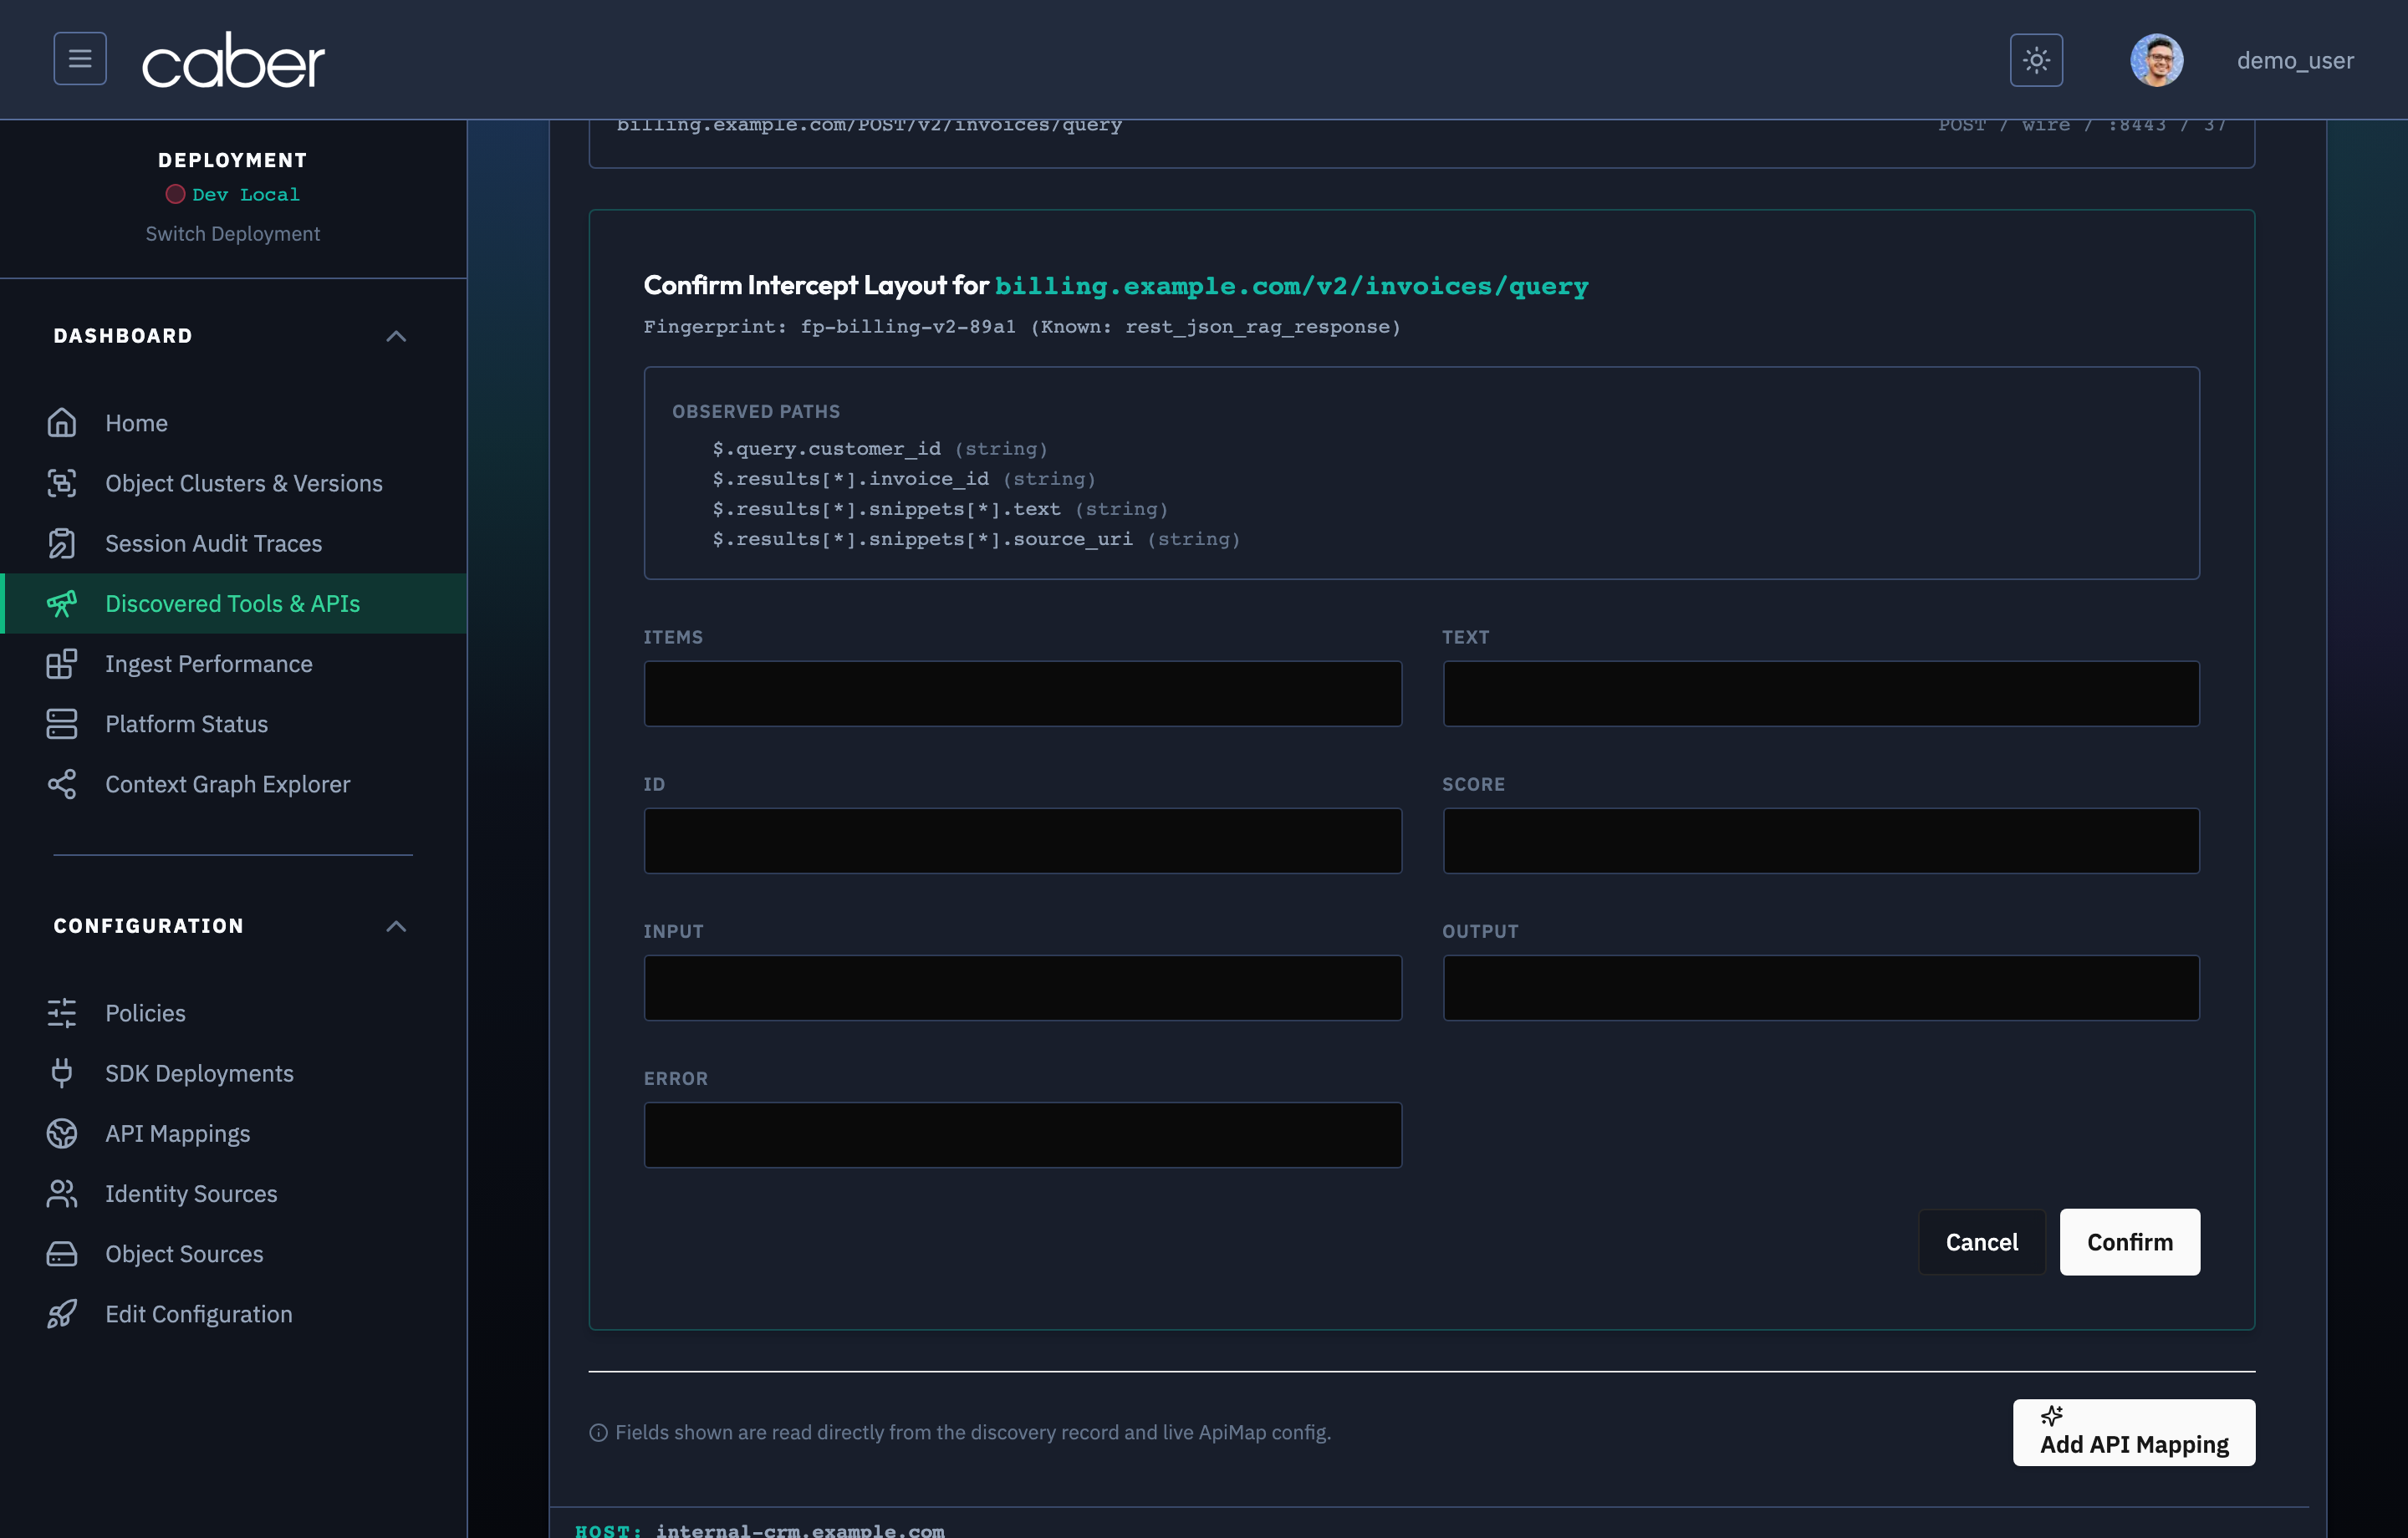
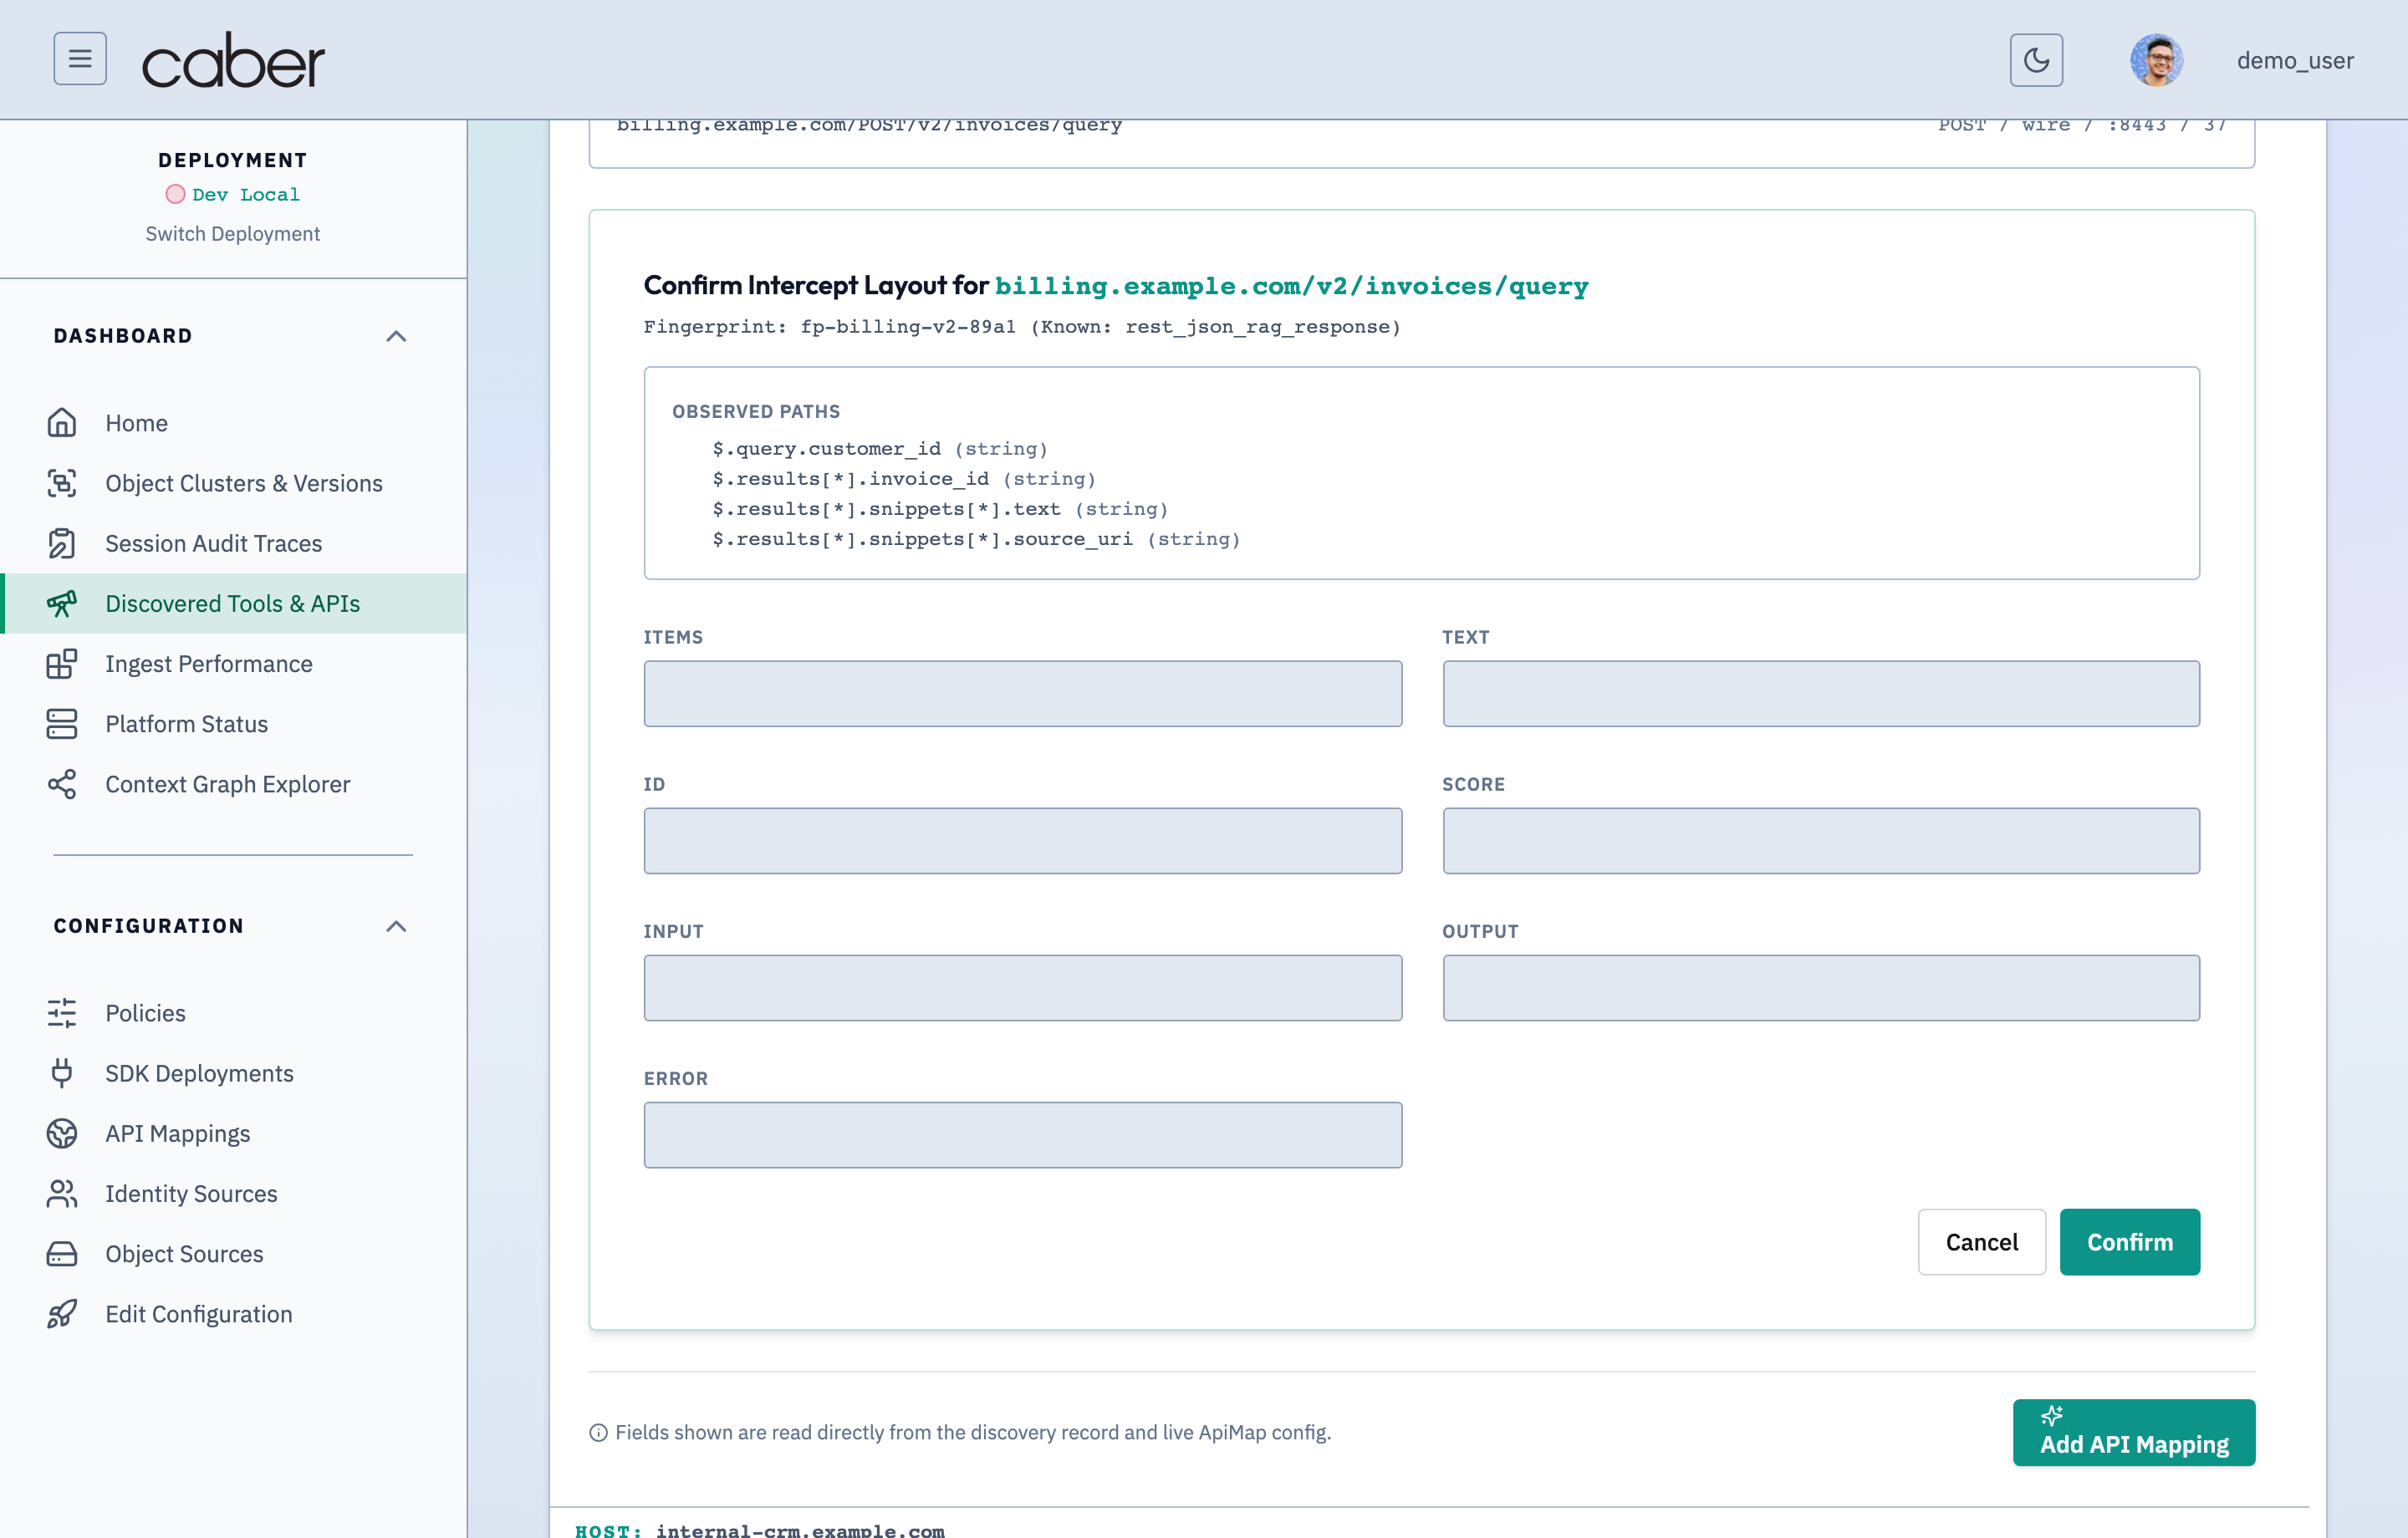
LayoutConfirmPanel) & Route Rules: Maps observed JSONPath payload fields to semantic extraction roles (ITEMS,TEXT,ID,SCORE,INPUT,OUTPUT,ERROR) and configures per hostroute_rulesin/admin/config/api-mappings. See API & Tool Interception for the step by step workflow.
/admin/discoveryConfirm Discovered Payload Layout & Field Role Binding ModalAssertion Verified: Proves that operators can review and confirm auto-detected payload field layouts (prompt text, response content, tool arguments, and OBO principal headers/claims) before activating inline interception.
5. Policy Studio, SDK Fleet & Source Configuration (/admin/config/*)
- Policy Studio (
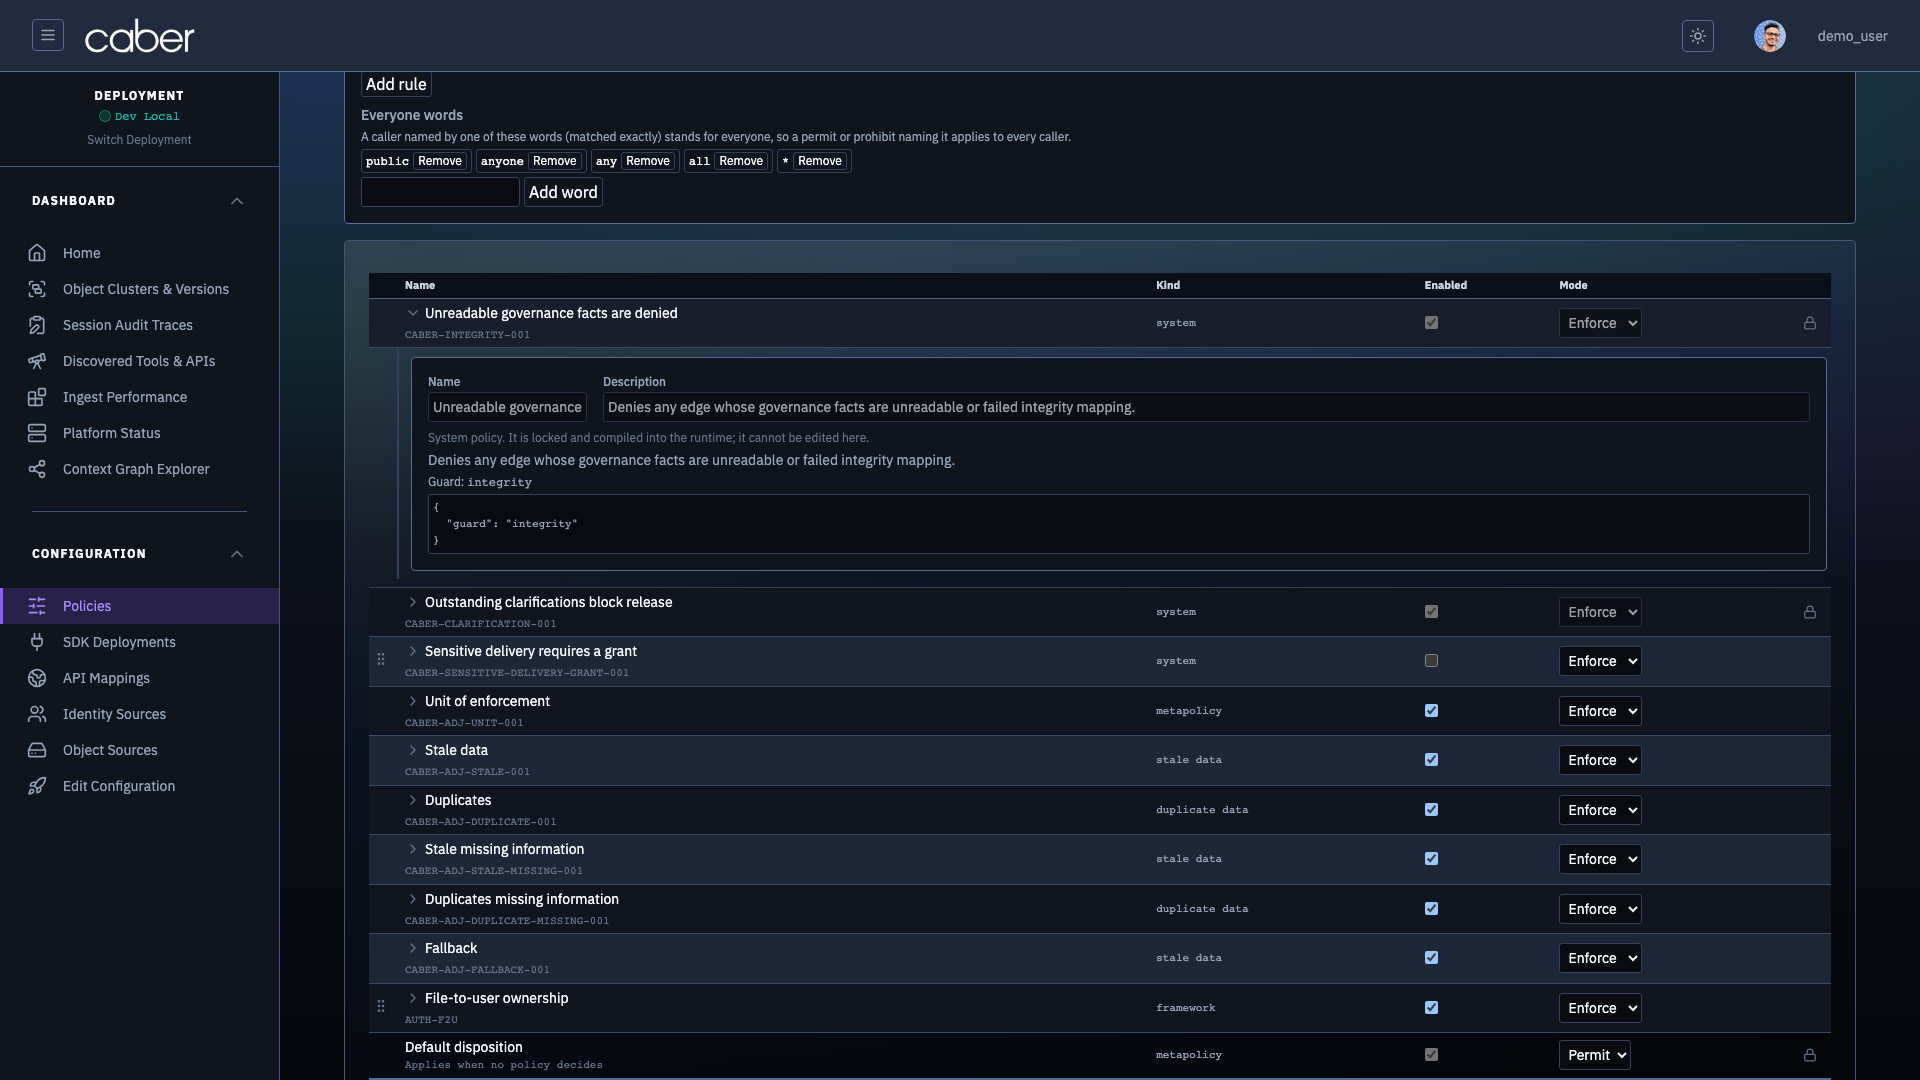
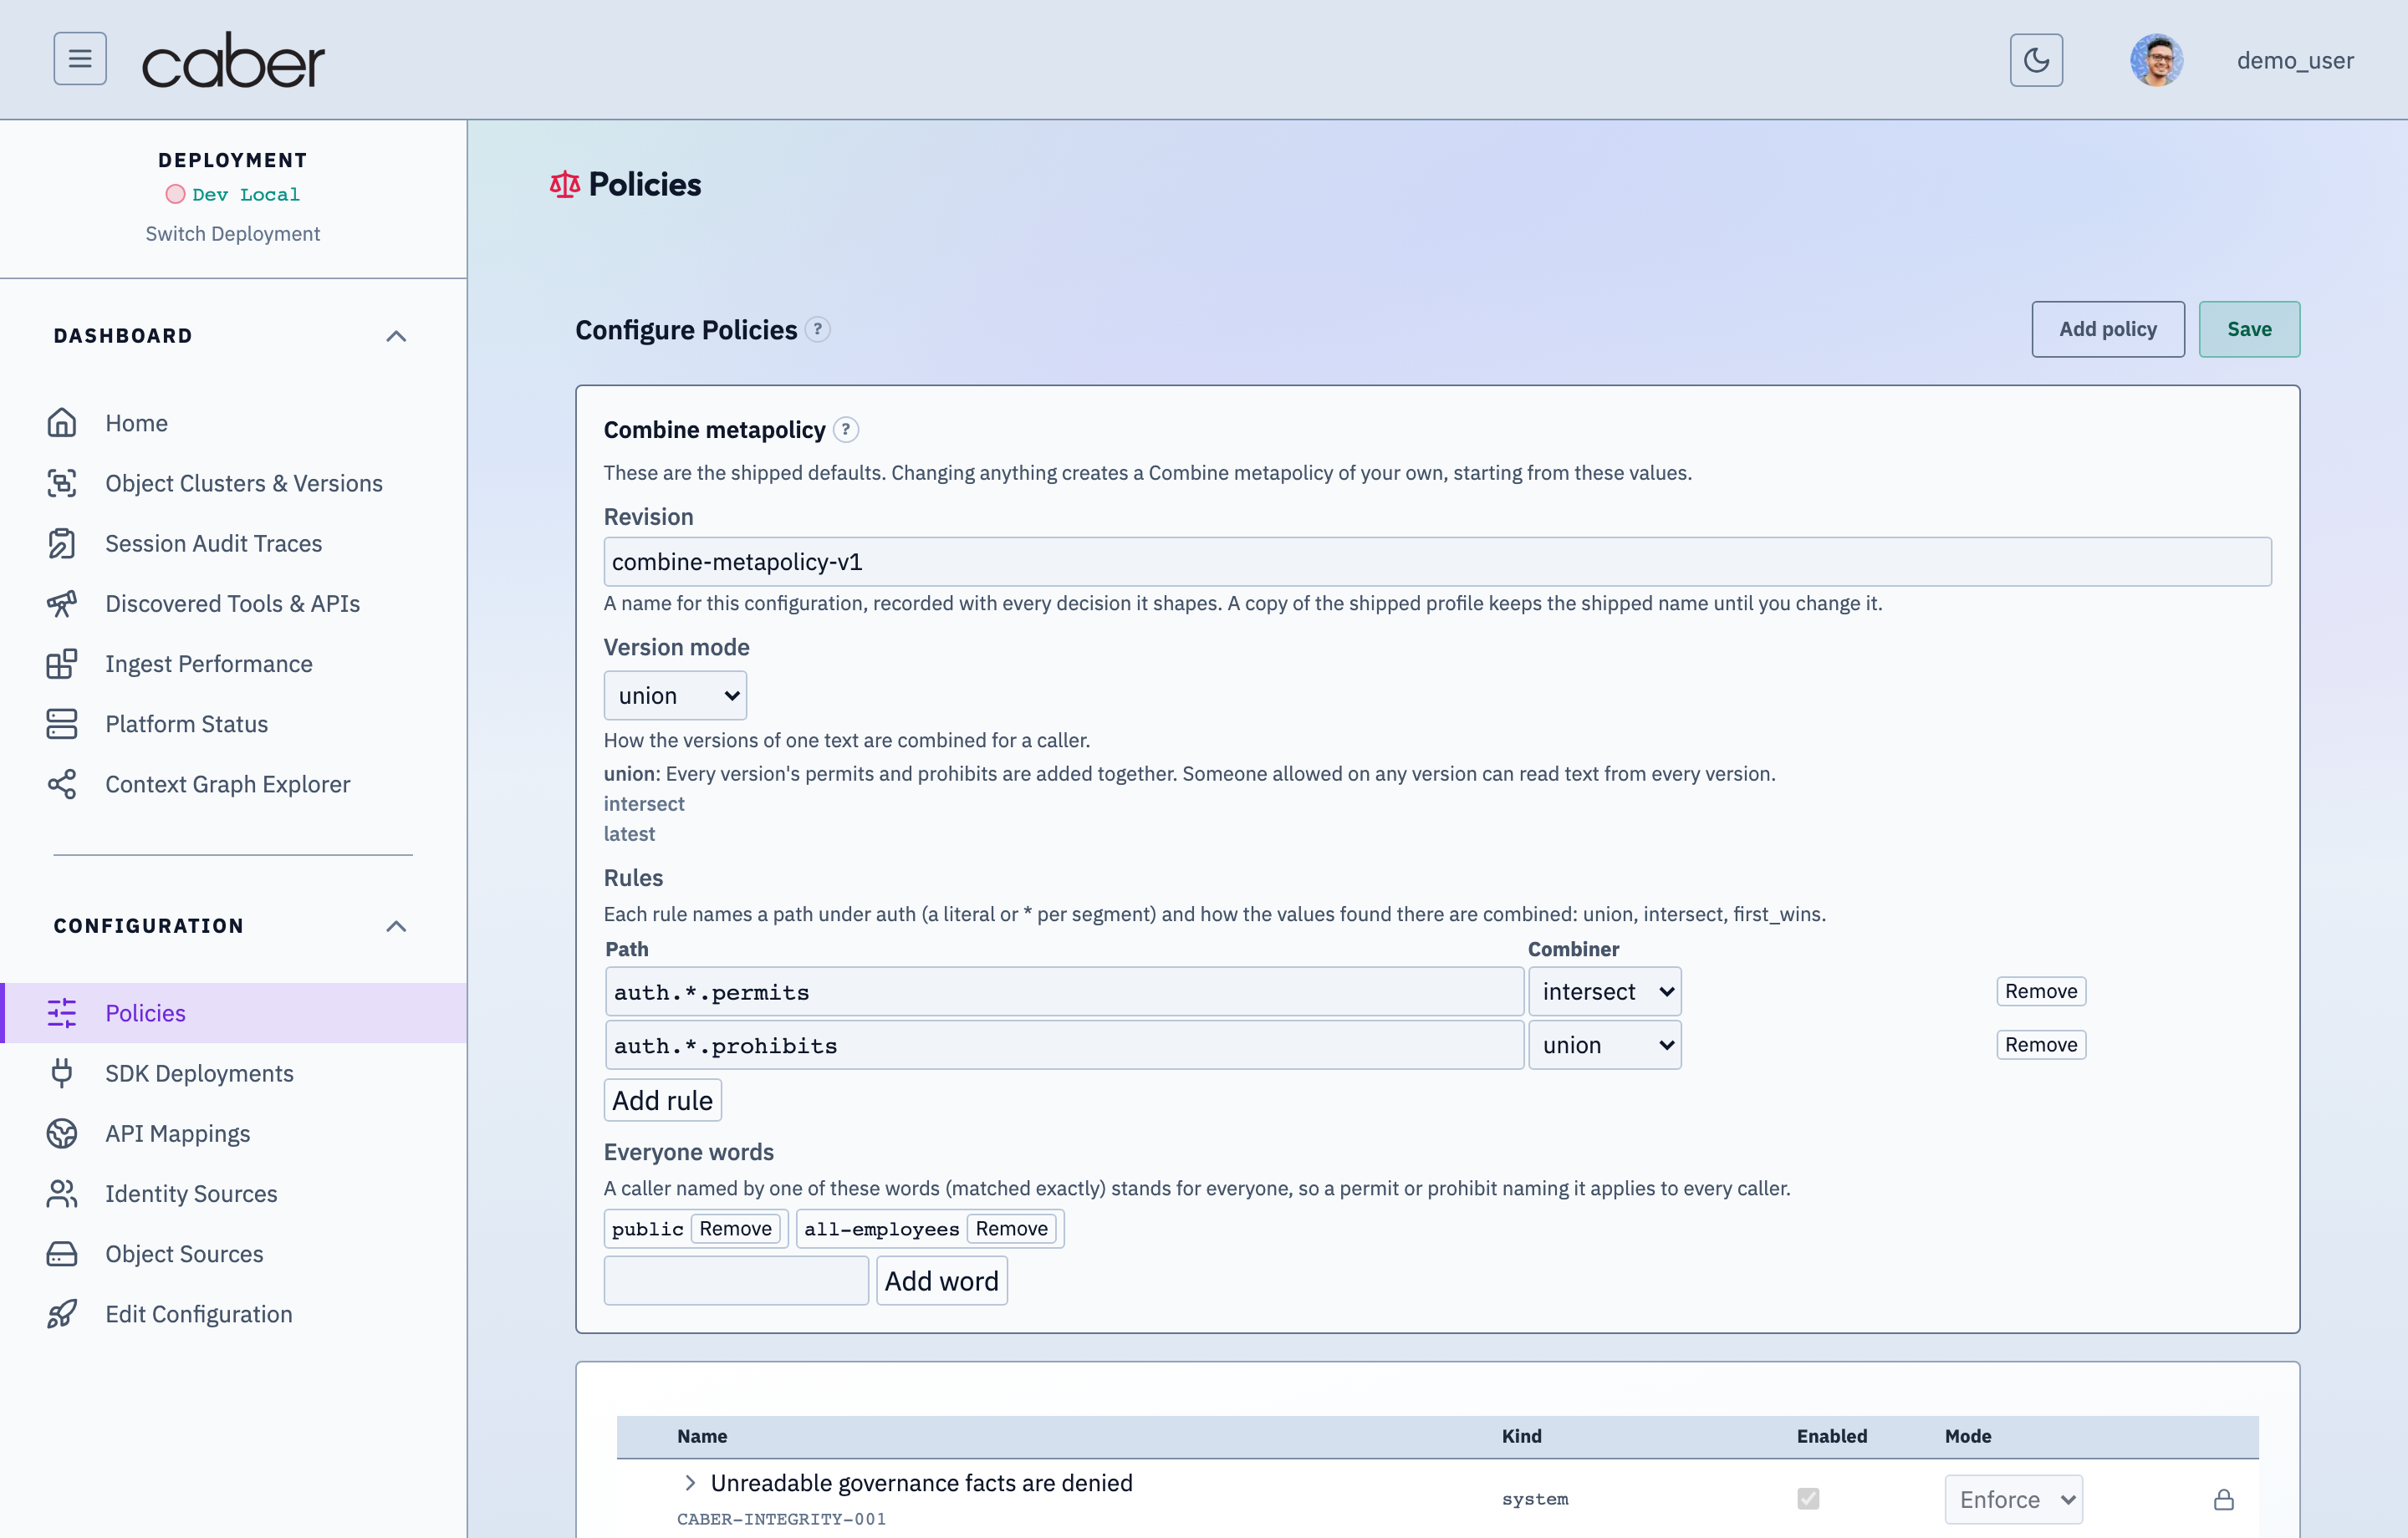
/admin/config/policies): Visual condition tree editor and compiler fordata_use,framework,object_auth_metapolicy,combine_metapolicy, andadjudication_metapolicyrules compiled into hot reloadedWasmbundles. - SDK Deployments, Identity & Object Sources, and AI Validation (
/admin/config/sdk-deployments,/admin/config/identity-sources,/admin/config/object-sources,/admin/config/review): Manages SDK service bindings, directory and bucket connectors, and AI assisted configuration validation. See Policy & Source Configuration.
/admin/config/policiesContract v3 Policy Studio & Verdict Snapshot v3 Diff InspectorAssertion Verified: Proves that Contract v3 Rego/Wasm policies and multisource metapolicies surgically redact only the unauthorized byte spans ([start, end) in source coordinate space) while preserving 94% of safe surrounding context in the response.
Backend for Frontend (BFF) Architecture
CaberUserConsole uses a dual layer Next.js architecture:
- Frontend Application (
src/pages/admin/*andsrc/components/admin/*): Built with React 19, Next.js 16, Tailwind CSS v4 semantic design tokens,next-themesdark and light mode polarity, Zustand stores, Cytoscape.js (cytoscape-elk), and Chart.js. - Next.js BFF API Layer (
src/pages/api/*): Authenticates operator requests, resolves active deployment context, and proxies queries across the Caber Control Plane, Neo4j (neo4j:7687), and MySQL operational stores.
6. Key Architecture Decisions & Design Rationale
- ADR 1: Next.js BFF Architecture vs Direct Browser to Database Connections: Allowing the browser to query control plane databases and Neo4j directly exposes credentials and bypasses authorization. The Next.js Backend for Frontend (
BFF) layer undersrc/pages/api/*handles session verification, deployment routing, and payload normalization. - ADR 2: Progressive Disclosure Dashboard Layout: Security dashboards often overwhelm operators with dense metrics.
CaberUserConsoleorganizes navigation into focusedDashboardandConfigurationworkspaces, pairing high level KPI cards with expandable operational drawers and slide in trace inspectors. - ADR 3: Integrated Discovery to Interception Pipeline: Rather than requiring operators to write JSONPath extraction rules blind,
/admin/discoverycaptures structural schema fingerprints from live traffic so operators can confirm semantic roles (LayoutConfirmPanel) and promote endpoints directly into/admin/config/api-mappings.